|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-289: mysql Vulnerability Assessment Details
|
RHSA-2002-289: mysql |
||
|
Check for the version of the mysql packages Detailed Explanation for this Vulnerability Assessment Updated packages are available for Red Hat Linux Advanced Server 2.1 that fix security vulnerabilities found in the MySQL server. [Updated 06 Feb 2003] Added fixed packages for Advanced Workstation 2.1 MySQL is a multi-user, multi-threaded SQL database server. While auditing MySQL, Stefan Esser found security vulnerabilities that can be used to crash the server or permit MySQL users to gain rights. A signed integer vulnerability in the COM_TABLE_DUMP package for MySQL 3.x to 3.23.53a, and 4.x to 4.0.5a, permits remote attackers to cause a denial of service (crash or hang) in mysqld by causing large negative integers to be provided to a memcpy call. (CVE-2002-1373) The COM_CHANGE_USER command in MySQL 3.x to 3.23.53a, and 4.x to 4.0.5a, permits a remote attacker to gain rights via a brute force attack using a one-character password, which causes MySQL to only compare the provided password against the first character of the real password. (CVE-2002-1374) The COM_CHANGE_USER command in MySQL 3.x to 3.23.53a, and 4.x to 4.0.5a, permits remote attackers to execute arbitrary code via a long response. (CVE-2002-1375) The MySQL client library (libmysqlclient) in MySQL 3.x to 3.23.53a, and 4.x to 4.0.5a, does not properly verify length fields for certain responses in the read_rows or read_one_row routines, which permits a malicious server to cause a denial of service and possibly execute arbitrary code. (CVE-2002-1376) Red Hat Linux Advanced Server 2.1 contains versions of MySQL that are vulnerable to these issues. All users of MySQL are advised to upgrade to these errata packages containing MySQL 3.23.54a which is not vulnerable to these issues. Solution : http://rhn.redhat.com/errata/RHSA-2002-289.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

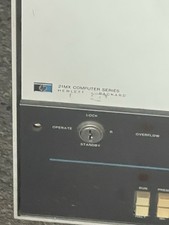
Vintage HP 21MX 1000 M-Series Minicomputer Chassis Backplane Parts AS-IS
$325.99
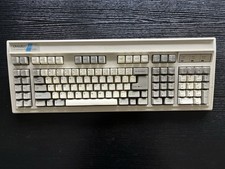
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
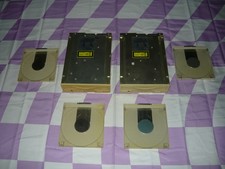
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
Sealed Vintage Intel Pro/1000 Network Adapters Drivers CD Ver 3.1 Vintage PC NEW
$39.61
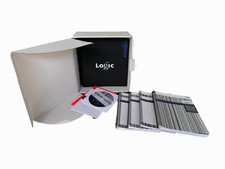
Vintage Emagic Logic 5 / Logic Audio 4.0 Studio Software Box Manuals Serial
$89.99
Original Vintage Old Style STANDARD Black CD Jewel Case (Heavy Duty) 90g Lot
$316.95
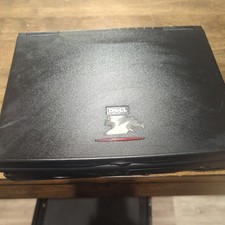
Dell Latitude XPi CD P150ST Vintage Computer - Not Working
$70.00
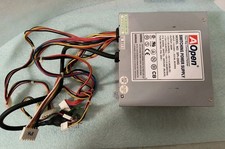
VINTAGE AOPEN MODEL SPI-200 200W AT POWER SUPPLY WITH SWITCH DS-PS-8
$34.95
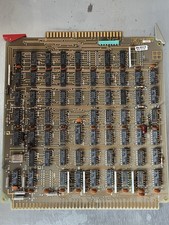
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
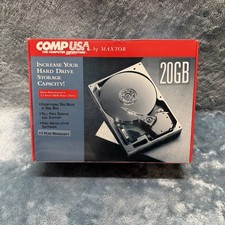
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
|
||
|
No Discussions have been posted on this vulnerability. |