|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-214: php Vulnerability Assessment Details
|
RHSA-2002-214: php |
||
|
Check for the version of the php packages Detailed Explanation for this Vulnerability Assessment PHP versions up to and including 4.2.2 contain vulnerabilities in the mail () function, permiting local script authors to bypass safe mode restrictions and possibly permiting remote attackers to insert arbitrary mail headers or content. [Updated 13 Jan 2003] Added fixed packages for the Itanium (IA64) architecture. [Updated 06 Feb 2003] Added fixed packages for Advanced Workstation 2.1 PHP is an HTML-embedded scripting language commonly used with the Apache HTTP server. The mail function in PHP 4.x to 4.2.2 may permit local script authors to bypass safe mode restrictions and modify command line arguments to the MTA (such as sendmail) in the 5th argument to mail(), altering MTA behavior and possibly executing arbitrary local commands. The mail function in PHP 4.x to 4.2.2 does not filter ASCII control characters from its arguments, which could permit remote attackers to modify mail message content, including mail headers, and possibly use PHP as a "spam proxy." Script authors should note that all input data should be checked for unsafe data by any PHP scripts which call functions such as mail(). Note that this PHP errata, as did RHSA-2002:129, enforces memory limits on the size of the PHP process to prevent a badly generated script from becoming a possible source for a denial of service attack. The default process size is 8Mb, though you can adjust this as you deem necessary through the php.ini directive memory_limit. For example, to change the process memory limit to 4MB, add the following: memory_limit 4194304 Important Note: There are special instructions you should follow regarding your /etc/php.ini configuration file in the "Solution" section below. Solution : http://rhn.redhat.com/errata/RHSA-2002-214.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

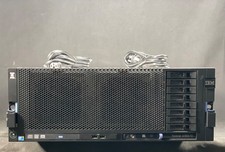
IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$179.99
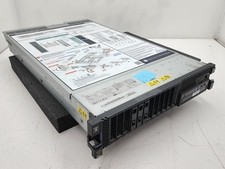
IBM Power 8 S822L Server 8247-22L POWER8 Enterprise 256GB RAM 2x 00KV626 CPU
$999.99
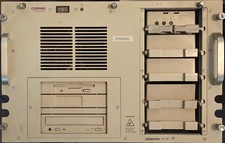
Compaq ProLiant 1500R 5/100 rack server, Series 3155, with IBM 2.1GB HD, VINTAGE
$295.00
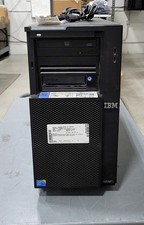
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$110.30
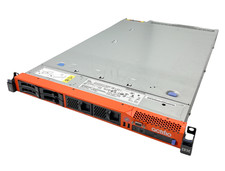
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$150.00
Rare Vintage IBM 93ZZ PowerPC Server Board - MCM Ceramic CPU - 40N1844 - 1.1 lbs
$49.99
Lot of 3 IBM 00JY196 ServeRAID M1210 PCI Express SAS SATA Storage Controller
$68.99
|
||
|
No Discussions have been posted on this vulnerability. |