|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-180: nss_ldap Vulnerability Assessment Details
|
RHSA-2002-180: nss_ldap |
||
|
Check for the version of the nss_ldap packages Detailed Explanation for this Vulnerability Assessment Updated nss_ldap packages are now available for Red Hat Linux Advanced Server 2.1. These updates fix a potential buffer overflow which can occur when nss_ldap is set to configure itself using information stored in DNS as well as a format string bug in logging functions used in pam_ldap. [Updated 09 Jan 2003] Added fixed packages for the Itanium (IA64) architecture. [Updated 06 Feb 2003] Added fixed packages for Advanced Workstation 2.1 nss_ldap is a set of C library extensions that permit X.500 and LDAP directory servers to be used as a primary source of aliases, ethers, groups, hosts, networks, protocols, users, RPCs, services, and shadow passwords (instead of or in addition to using flat files or NIS). When versions of nss_ldap prior to nss_ldap-198 are configured without a value for the "host" setting, nss_ldap will attempt to configure itself by using SRV records stored in DNS. When parsing the results of the DNS query, nss_ldap does not check that data returned by the server will fit into an internal buffer, leaving it vulnerable to a buffer overflow The Common Vulnerabilities and Exposures project has assigned the name CVE-2002-0825 to this issue. When versions of nss_ldap prior to nss_ldap-199 are configured without a value for the "host" setting, nss_ldap will attempt to configure itself by using SRV records stored in DNS. When parsing the results of the DNS query, nss_ldap does not check that the data returned has not been truncated by the resolver libraries to avoid a buffer overflow, and may attempt to parse more data than is actually available, leaving it vulnerable to a read buffer overflow. Versions of pam_ldap prior to version 144 include a format string bug in the logging function. The packages included in this erratum update pam_ldap to version 144, fixing this bug. The Common Vulnerabilities and Exposures project has assigned the name CVE-2002-0374 to this issue. All users of nss_ldap should update to these errata packages which are not vulnerable to the above issues. These packages are based on nss_ldap-189 with the addition of a backported security patch and pam_ldap version 144. Thanks to the nss_ldap and pam_ldap team at padl.com for providing information about these issues. Solution : http://rhn.redhat.com/errata/RHSA-2002-180.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

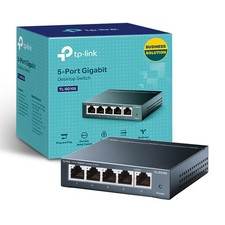
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
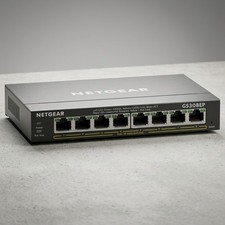
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
TP-Link TL-SG105, 5 Port Gigabit Unmanaged Ethernet Switch, Network Hub, Ethern
$15.25
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Linksys LGS328MPC 24-Port Managed Gigabit PoE+ Switch with 4 10G SFP+ Uplinks
$224.95
|
||
|
No Discussions have been posted on this vulnerability. |