|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-167: glibc Vulnerability Assessment Details
|
RHSA-2002-167: glibc |
||
|
Check for the version of the glibc packages Detailed Explanation for this Vulnerability Assessment Updated glibc packages are available which fix a buffer overflow in the XDR decoder and two vulnerabilities in the resolver functions. [updated 8 aug 2002] Updated packages have been made available, as the original errata introduced a bug which could cause calloc() to crash on 32-bit platforms when passed a size of 0. These updated errata packages contain a patch to correct this bug. The glibc package contains standard libraries which are used by multiple programs on the system. Sun RPC is a remote procedure call framework which permits clients to invoke procedures in a server process over a network. XDR is a mechanism for encoding data structures for use with RPC. NFS, NIS, and other network services that are built upon Sun RPC. The glibc package contains an XDR encoder/decoder derived from Sun's RPC implementation which was recently demonstrated to be vulnerable to a heap overflow. An error in the calculation of memory needed for unpacking arrays in the XDR decoder can result in a heap buffer overflow in glibc 2.2.5 and earlier. Depending upon the application, this vulnerability may be exploitable and could lead to arbitrary code execution. (CVE-2002-0391) A buffer overflow vulnerability has been found in the way the glibc resolver handles the resolution of network names and addresses via DNS (as per Internet RFC 1011). Version 2.2.5 of glibc and earlier versions are affected. A system would be vulnerable to this issue if the "networks" database in the /etc/nsswitch.conf file includes the "dns" entry. By default, Red Hat Linux Advanced Server ships with "networks" set to "files" and is therefore not vulnerable to this issue. (CVE-2002-0684) A related issue is a bug in the glibc-compat packages, which provide compatibility for applications compiled against glibc version 2.0.x. Applications compiled against this version (such as those distributed with early Red Hat Linux releases 5.0, 5.1, and 5.2) could also be vulnerable to this issue. (CVE-2002-0651) All users should upgrade to these errata packages which contain patches to the glibc libraries and therefore are not vulnerable to these issues. Thanks to Solar Designer for providing patches for this issue. Solution : http://rhn.redhat.com/errata/RHSA-2002-167.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$179.99
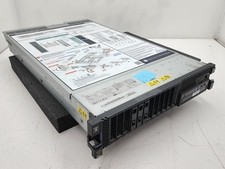
IBM Power 8 S822L Server 8247-22L POWER8 Enterprise 256GB RAM 2x 00KV626 CPU
$999.99
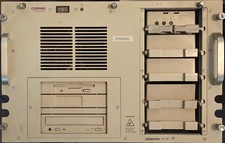
Compaq ProLiant 1500R 5/100 rack server, Series 3155, with IBM 2.1GB HD, VINTAGE
$295.00
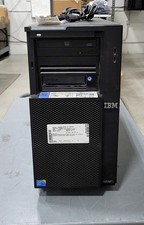
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$110.30
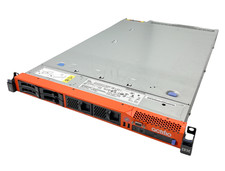
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$150.00
Rare Vintage IBM 93ZZ PowerPC Server Board - MCM Ceramic CPU - 40N1844 - 1.1 lbs
$49.99
Lot of 3 IBM 00JY196 ServeRAID M1210 PCI Express SAS SATA Storage Controller
$68.99
|
||
|
No Discussions have been posted on this vulnerability. |