|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-161: openssl Vulnerability Assessment Details
|
RHSA-2002-161: openssl |
||
|
Check for the version of the openssl packages Detailed Explanation for this Vulnerability Assessment Updated OpenSSL packages are available for Red Hat Linux Advanced Server. These updates fix multiple protocol parsing bugs, which may cause a denial of service (DoS) attack or cause SSL-enabled applications to crash. [Updated 06 Jan 2003] Added fixed packages for the ia64 architecture. [Updated 06 Feb 2003] Added fixed packages for Advanced Workstation 2.1 OpenSSL is a commercial-grade, full-featured, and open source toolkit which implements the Secure Sockets Layer (SSL v2/v3) and Transport Layer Security (TLS v1) protocols as well as a full-strength general purpose cryptography library. Portions of the SSL protocol data stream, which include the lengths of structures which are being transferred, may not be properly validated. This may permit a malicious server or client to cause an affected application to crash or enter an infinite loop, which can be used as a denial of service (DoS) attack if the application is a server. It has not been verified if this issue could lead to further consequences such as remote code execution. These errata packages contain a patch to correct this vulnerability. Please note that the original patch from the OpenSSL team had a mistake in it which could possibly still permit buffer overflows to occur. This bug is also fixed in these errata packages. NOTE: Please read the Solution section below as it contains instructions for making sure that all SSL-enabled processes are restarted after the update is applied. Thanks go to the OpenSSL team for providing patches for these issues. Solution : http://rhn.redhat.com/errata/RHSA-2002-161.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

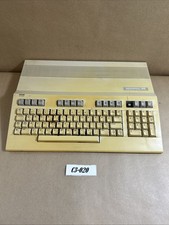
Commodore 128 C128 Computer FOR PARTS / REPAIR Untested Missing Key No Cords
$149.99
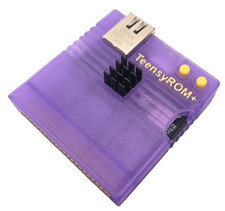
TeensyROM+ TR+ v0.4 Cartridge for C64/128 - w/ Case & 32GB SD Preloaded
$89.50
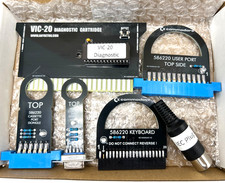
Commodore VIC-20 Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
RARE Commodore MPS801 Printer - 1st printer for the 64 - powers on
$70.00
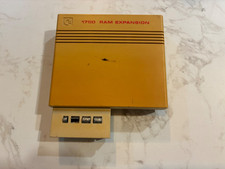
Commodore 1750 512K RAM Expansion REU for C128 / C64 – Tested & Working
$110.00
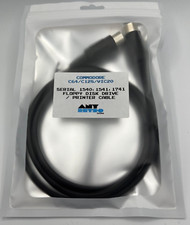
Commodore 64 Serial Cable 6PIN DIN 1541 1571 C64 128 C128 Disk Drive Printer USA
$10.49
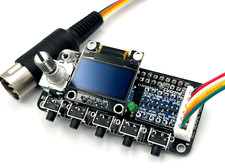
Commodore 1541 Emulator PI1541 HAT with ROTARY, OLED screen, USA Seller
$29.99
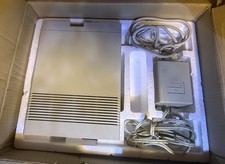
Vtg 128 / 64 Commodore 1541-II Computer Disk Drive in Box 5.25 Floppy (Working)
$89.99
Commodore 64 Dead Test & Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
Commodore 64 Drive Alignment & Utility Diskette
$9.99
|
||
|
No Discussions have been posted on this vulnerability. |