|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-137: util Vulnerability Assessment Details
|
RHSA-2002-137: util |
||
|
Check for the version of the util packages Detailed Explanation for this Vulnerability Assessment The util-linux package shipped with Red Hat Linux Advanced Server contains a locally exploitable vulnerability. The util-linux package contains a large variety of low-level system utilities that are necessary for a Linux system to function. The 'chfn' utility included in this package permits users to modify personal information stored in the system-wide password file, /etc/passwd. In order to modify this file, this application is installed setuid root. Under certain conditions, a carefully crafted attack sequence can be performed to exploit a complex file locking and modification race present in this utility permiting changes to be made to /etc/passwd. In order to successfully exploit the vulnerability and perform privilege escalation there is a need for a minimal administrator interaction. Additionally, the password file must be over 4 kilobytes, and the local attackers entry must not be in the last 4 kilobytes of the password file. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2002-0638 to this issue. An interim workaround is to remove setuid flags from /usr/bin/chfn and /usr/bin/chsh. All users of Red Hat Linux should update to the errata util-linux packages which contain a patch to correct this vulnerability. Many thanks to Michal Zalewski of Bindview for alerting us to this issue. Solution : http://rhn.redhat.com/errata/RHSA-2002-137.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00
Western Digital 0B36404 Ultrastar DC HC320 8TB 7200RPM SATA HDD, HUS728T8TALE6L4
$250.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
Seagate Exos ST20000NM003C 20TB CMR 7200RPM SATA6Gb/s 3.5" Enterprise Hard Drive
$509.99
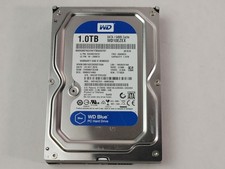
Western Digital WD Blue WD10EZEX 1 TB 3.5" SATA III Desktop Hard Drive
$23.99
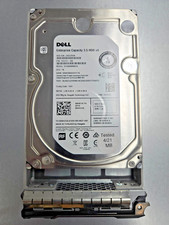
Dell ST6000NM0034 1HT27Z-150 NWCCG 6TB SAS 3.5 7.2K ENTERPRISE SERVER DRIVE
$68.99
Seagate Exos ST2000NX0253 HDD 2TB SATA 7.2K 2.5" 512b/s
$55.00
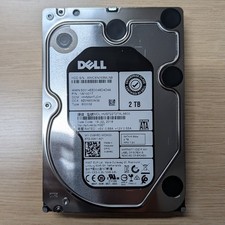
DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95
(ST8000NM0045) SEAGATE ENTERPRISE 8TB 7200RPM 4Kn SATA 6Gb/s 3.5" HARD DRIVE
$199.99
|
||
|
No Discussions have been posted on this vulnerability. |