|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-136: mod_ssl Vulnerability Assessment Details
|
RHSA-2002-136: mod_ssl |
||
|
Check for the version of the mod_ssl packages Detailed Explanation for this Vulnerability Assessment Updated mod_ssl packages are now available for Red Hat Advanced Server. These updates incorporate a fix for an incorrect bounds check in versions of mod_ssl up to and including version 2.8.9. The mod_ssl module provides strong cryptography for the Apache Web server via the Secure Sockets Layer (SSL) and Transport Layer Security (TLS) protocols. Versions of mod_ssl prior to 2.8.10 are subject to a single NULL overflow that can cause arbitrary code execution. In order to exploit this vulnerability, the Apache Web server has to be configured to permit overriding of configuration settings on a per-directory basis, and untrusted local users must be able to modify a directory in which the server is configured to permit overriding. The local attacker may then become the user that Apache is running as (usually 'www' or 'nobody'). Note that regardless of this bug, local users can obtain the same rights if the server is configured to permit them to create CGI scripts which run as the Web server user, or if PHP is enabled but not configured in "safe mode". The errata packages contain versions of mod_ssl that have been patched and are not vulnerable to this issue. Please note that you must restart the httpd daemon to use the updated module. For instructions on doing this, see the bottom of the Solutions section below. Solution : http://rhn.redhat.com/errata/RHSA-2002-136.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

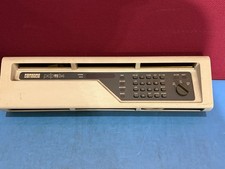
DEC PDP-11/34 Front Panel Complete PDP11 RARE
$450.00
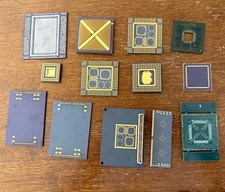
Vintage Intel Mainframe Server MCM CPU Substrate Lot Prototyping PGA Validation
$500.00
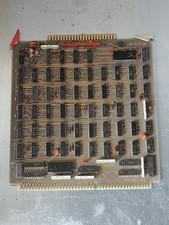
HP 13210-60001 Disc Drive Interface PCB HP 7900A 7901A Vintage
$225.61
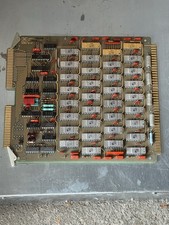
HP 5060-8359 8K Semiconductor Memory Module 5080-9747 Vintage HP Computer
$224.72
Vtg IBM Mainframe Prototype Chip Module Lot 146 pc 1988-1993 ES/9000 Lab Arcive
$649.00
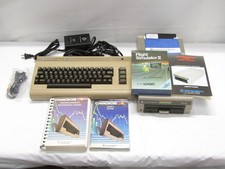
Commodore 64 PC with Model 1541 Diskette Drive and Flight Simulator II *READ*
$199.99
Vintage Mainframe Computer Disk Drive Pack Dyson SMD 5 Level Disks
$79.00
Rare Vintage Mainframe Burroughs Discrete-Transistor Cordwood Module B2500/B5000
$99.95
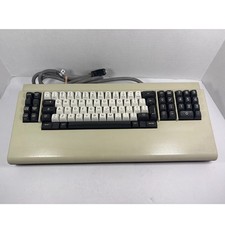
Vintage Telex 952003-112 Mechanical Terminal Keyboard IBM 3270 Mainframe DB25
$799.00
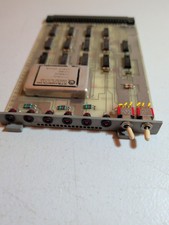
Vintage UNIVAC 3620670-01 Mainframe Logic Board 15MHz Sperry Computer PCB
$98.95
|
||
|
No Discussions have been posted on this vulnerability. |