|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-129: php Vulnerability Assessment Details
|
RHSA-2002-129: php |
||
|
Check for the version of the php packages Detailed Explanation for this Vulnerability Assessment PHP versions earlier than 4.1.0 contain a vulnerability that could permit arbitrary commands to be executed. [updated 22 Aug 2002] The initial set of errata packages contained an incorrect set of dependencies. This meant that a number of packages would need to be installed before php that were not essential to the operation of php. Updated errata packages are included with this advisory that have corrected dependencies. PHP is an HTML-embedded scripting language commonly used with Apache. PHP versions 4.0.5 through 4.1.0 in safe mode do not properly cleanse the 5th parameter to the mail() function. This vulnerability permits local users and possibly remote attackers to execute arbitrary commands via shell metacharacters. Red Hat Linux Advanced Server version 2.1 shipped with PHP 4.0.6. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2001-1246 to this issue. All users of PHP should upgrade to these errata packages containing PHP 4.1.2, which is not vulnerable to this issue. Note: This PHP errata enforces memory limits on the size of the PHP process to prevent a badly generated script from becoming a possible source for a denial of service attack. The default process size is 8Mb though you can adjust this as you deem necessary thought the php.ini directive memory_limit. For example, to change the process memory limit to 4MB, add the following: memory_limit 4194304 Important Installation Note: There are special instructions you should follow regarding your /etc/php.ini configuration file in the "Solution" section below. Solution : http://rhn.redhat.com/errata/RHSA-2002-129.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

GIGABYTE A520M DS3H AC AMD AM4 Motherboard mATX
$59.99
GIGABYTE Z790 AORUS ELITE AX LGA 1700 Intel Z790 ATX Motherboard with DDR5
$189.99
Intel H310 LGA1151 8-9th Gen DDR4 M.2 NVMe mATX Motherboard IO Shield Battery
$54.99
ASUS PRIME Z490-V Motherboard Intel Z490 10th gen DDR4 LGA 1200 ATX w/ IO Shield
$84.99
GIGABYTE B365 HD3 LGA1151 Intel 9th Gen motherboard
$59.99
Intel H81 Motherboard M.2 NVMe LGA 1150 mATX w/ IO Shield (Random Slot Color)
$29.90
ASUS PRIME B360M-C MicroATX Intel LGA1151 DDR4 HDMI VGA USB RJ-45 Audio
$34.99
ASUS PRIME Z370-A II LGA 1151 Intel Z370 DDR4 DIMM USB3.1 DVI ATX RGB
$69.99
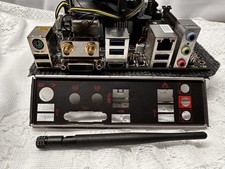
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
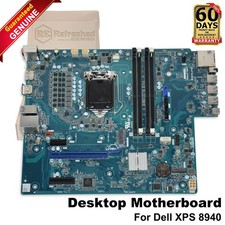
Dell XPS 8940 Desktop Motherboard Intel H470 LGA1200 DDR4 K3CM7 KV3RP 427JK
$154.99
|
||
|
No Discussions have been posted on this vulnerability. |