|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-120: LPRng Vulnerability Assessment Details
|
RHSA-2002-120: LPRng |
||
|
Check for the version of the LPRng packages Detailed Explanation for this Vulnerability Assessment The LPRng print spooler, as shipped in Red Hat Linux Advanced Server 2.1, accepts all remote print jobs by default. Updated LPRng packages are available to fix this issue. With its default configuration, LPRng will accept job submissions from any host, which is not appropriate in a workstation environment. We are grateful to Matthew Caron for pointing out this configuration problem. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2002-0378 to this issue. The updated packages from this advisory change the job submission policy (in /etc/lpd.perms) so that jobs from remote hosts are refused by default. Those running print servers may want to adjust this policy as appropriate, for example to give access to certain hosts or subnets. For details on how to do this, see the lpd.perms(5) man page. Please note that default installations of Red Hat Linux Advanced Server 2.1 include ipchains rules blocking remote access to the print spooler IP port as a result those installations already reject remote job submissions. NOTE: There are special instructions for installing this update at the end of the "Solution" section. Solution : http://rhn.redhat.com/errata/RHSA-2002-120.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$155.00
pfSense Firewall 16-Core Atom C3958 8GB DDR4 RAM 64GB SSD 8x 1Gbe QAT AES-NI VPN
$184.99
OPNsense pfSense 16-Core Atom C3958 16GB ECC RAM 512GB SSD 8-Port QAT AES-NI VPN
$248.00
SonicWall TZ280 Firewall 03-SSC-6933 Advanced Edition 3YR NEW SEALED
$999.99
Fortinet FortiGate 60F FG-60F P24286-03-13 Network Firewall Security Appliance
$155.75
Palo Alto PA-220 Next-Gen Firewall 520-000309-00J
$40.00
Fortinet FortiGate 60F FG-60F UTM UTP License Until 2027 Network Security FW VPN
$239.99
Fortinet FortiGate 80E 12 Ports Firewall Appliance
$20.25
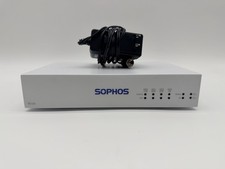
Sophos SG 115 rev.3 Firewall Security Appliance SG1153BAEUS + OPNsense
$85.00
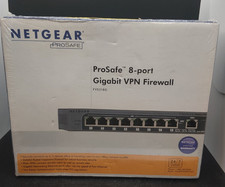
NETGEAR ProSafe 8-Port Gigabit VPN Firewall FVS318G NEW IN BOX
$69.99
|
||
|
No Discussions have been posted on this vulnerability. |