|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2002-119: bind Vulnerability Assessment Details
|
RHSA-2002-119: bind |
||
|
Check for the version of the bind packages Detailed Explanation for this Vulnerability Assessment Version 9 of ISC BIND, prior to version 9.2.1, contained a denial of service (DoS) attack vulnerability. Various versions of the ISC BIND resolver libraries are vulnerable to a buffer overflow attack. ISC BIND (Berkeley Internet Name Domain) is an implementation of the DNS (Domain Name System) protocols. BIND includes a DNS server (named) -- which resolves hostnames to IP addresses, a resolver library (routines for applications to use when interfacing with DNS), and various tools. Versions of BIND 9 prior to 9.2.1 have a bug that causes certain requests to the BIND name server to fail an internal consistency check, causing the name server to stop responding to requests. This can be used by a remote attacker to cause a denial of service (DoS) attack against name servers. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2002-0400 to this issue. A buffer overflow vulnerability exists in multiple implementations of DNS resolver libraries. Applications that utilize vulnerable DNS resolver libraries may be affected. A remote attacker who is able to send malicious DNS responses could potentially exploit this vulnerability to execute arbitrary code or cause a denial of service (DoS) attack on a vulnerable system. Red Hat Linux does not ship with any applications or libraries that link against the BIND resolver libraries however, third party code may be affected. (CVE-2002-0651) Red Hat Linux Advanced Server shipped with a version of ISC BIND vulnerable to both of these issues. All users of BIND are advised to upgrade to the errata packages containing BIND 9.2.1 which contains backported patches that correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2002-119.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
Samsung 64GB PC4-2666V-R 2S2Rx4 DDR4 ECC REG RDIMM - M393A8K40B22-CWD6Y
$270.00
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
Lot 500 SK hynix 16GB 2Rx8 PC4-23400 DDR4-2933Y ECC Registered Server Memory RAM
$47988.00
Corsair Vengeance DDR3 8GB 16GB 32GB 1866MHz PC3-14900 Desktop RAM Memory DIMM
$85.00
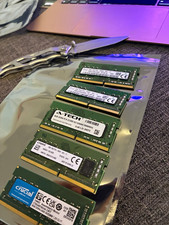
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
|
||
|
No Discussions have been posted on this vulnerability. |