|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Databases >> Oracle 9iAS SOAP Default Configuration Vulnerability Vulnerability Assessment Details
|
Oracle 9iAS SOAP Default Configuration Vulnerability |
||
|
Tests for Oracle9iAS default SOAP installation Detailed Explanation for this Vulnerability Assessment In a default installation of Oracle 9iAS v.1.0.2.2, it is possible to deploy or undeploy SOAP services without the need of any kind of credentials. This is due to SOAP being enabled by default after installation in order to provide a convenient way to use SOAP samples. However, this feature poses a threat to HTTP servers with public access since remote attackers can create soap services and then invoke them remotely. Since SOAP services can contain arbitrary Java code in Oracle 9iAS this means that a possible hacker can execute arbitray code in the remote server. Solution: Disable SOAP or the deploy/undeploy feature by editing $ORACLE_HOME/Apache/Jserver/etc/jserv.conf and removing/commenting the following four lines: ApJServGroup group2 1 1 $ORACLE_HOME/Apache/Jserv/etc/jservSoap.properties ApJServMount /soap/servlet ajpv12://localhost:8200/soap ApJServMount /dms2 ajpv12://localhost:8200/soap ApJServGroupMount /soap/servlet balance://group2/soap Note that the port number might be different from 8200. Also, you will need to change in the file $ORACLE_HOME/soap/werbapps/soap/WEB-INF/config/soapConfig.xml: to More information: http://otn.oracle.com/deploy/security/pdf/ias_soap_alert.pdf http://www.cert.org/advisories/CA-2002-08.html http://www.kb.cert.org/vuls/id/476619 Also read: Hackproofing Oracle Application Server from NGSSoftware: available at http://www.nextgenss.com/papers/hpoas.pdf Network Security Threat Level: High Networks Security ID: 4289 Vulnerability Assessment Copyright: This script is Copyright (C) 2003 Javier Fernandez-Sanguino |
||
|
Cables, Connectors |

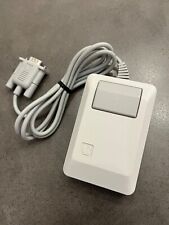
Macintosh Platinum Mouse - Apple 128K 512K 512Ke Mac Plus Lisa IIe M0100 - NEW
$49.99
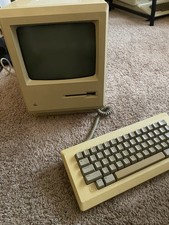
Apple Macintosh 128k Desktop computer. Upgraded to 512k
$300.00
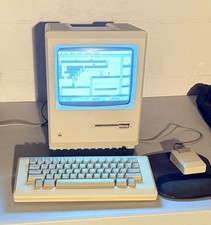
1984 APPLE MACINTOSH 128K MATCHING # BOX Set Original Mac Model M0001 WORKS RARE
$6299.00

1984 APPLE MACINTOSH 128K FIRST MAC Model M0001 PICASSO KIT Discs Harvard Rare
$1800.00
Macintosh Platinum Mouse - Apple 128K 512K 512Ke Mac Plus Lisa IIe M0100 - NEW
$59.99
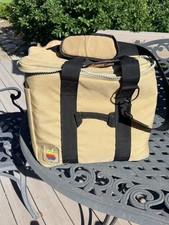
Vintage Apple Macintosh 128K 512K Carrying Case Rainbow Logo Excellent Cond
$140.00
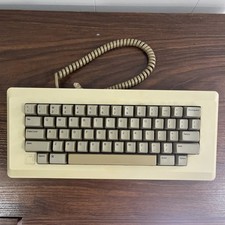
Apple Keyboard and Cable for Macintosh 128k 512k Mac Plus RARE Vintage M0110
$129.99
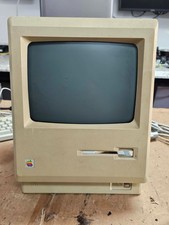
Vintage Early Week 12 1984 Apple Macintosh 128K Computer M0001 w/Analog Board+
$209.99
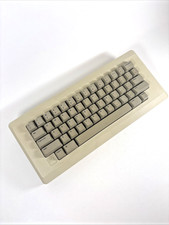
Apple Keyboard for Macintosh 128k 512k Mac Plus RARE Vintage M0110 (010)
$149.00
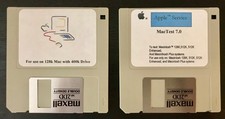
Apple Macintosh Mac 128k - 512k Boot / Diagnostics 2 Disk Set for Classic Macs
$14.99
|
||
|
No Discussions have been posted on this vulnerability. |