|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Remote file access >> Mailman private.py Directory Traversal Vulnerability Vulnerability Assessment Details
|
Mailman private.py Directory Traversal Vulnerability |
||
|
Checks for Mailman private.py Directory Traversal Vulnerability Detailed Explanation for this Vulnerability Assessment Summary : Authenticated Mailman users can view arbitrary files on the remote host. Description : According to its version number, the remote installation of Mailman reportedly is prone to a directory traversal vulnerability in 'Cgi/private.py'. The flaw comes into play only on web servers that don't strip extraneous slashes from URLs, such as Apache 1.3.x, and permits a list subscriber, using a specially crafted web request, to retrieve arbitrary files from the server - any file accessible by the user under which the web server operates, including email addresses and passwords of subscribers of any lists hosted on the server. For example, if '$user' and '$pass' identify a subscriber of the list '$listname@$target', then the following URL : http://$target/mailman/private/$listname/.../....///mailman?username=$user&password=$pass permits access to archives for the mailing list named 'mailman' for which the user might not otherwise be entitled. See also : http://mail.python.org/pipermail/mailman-announce/2005-February/000076.html http://lists.netsys.com/pipermail/full-disclosure/2005-February/031562.html Solution : Upgrade to Mailman 2.1.6b1 or apply the fix referenced in the first URL above. Network Security Threat Level: Low / CVSS Base Score : 2 (AV:R/AC:H/Au:R/C:P/A:N/I:N/B:C) Networks Security ID: 12504 Vulnerability Assessment Copyright: This script is Copyright (C) 2005 George A. Theall |
||
|
Cables, Connectors |

AMD Ryzen 5 5500 Processor ( read Description)
$59.00
(LOT OF 20) Intel Core i5-8400 CPU 2.80GHz Desktop Processor (SR3QT)
$700.00
INTEL CORE I9-10940X X-SERIES PROCESSOR | 3.30GHZ | SRGSH
$179.99
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
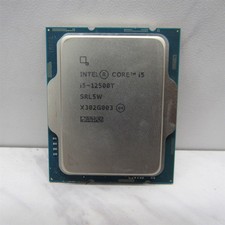
Intel Core i5-12500T SRL5W 2GHz 18MB 6 Core Socket LGA1700 Desktop CPU Processor
$114.99
Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
Intel Core i7-3770K 3.5 GHz Processor
$39.00
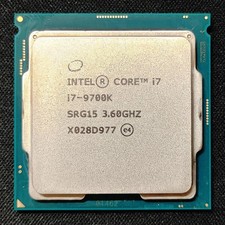
Intel Core i7-9700K Octa-Core 3.6 GHz Desktop CPU
$99.99
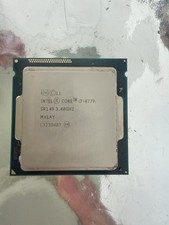
Intel Core i7-4770 3.40GHz Quad Core SR149 LGA 1150 CPU Processor tested
$35.00
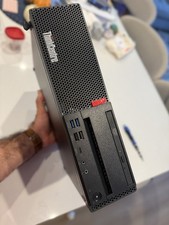
Lenovo ThinkCentre M920s SFF Barebones PC Motherboard PSU DVD No CPU RAM SSD
$27.99
|
||
|
No Discussions have been posted on this vulnerability. |