|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gain root remotely >> MailEnable IMAP Server Buffer Overflow and Directory Traversal Vulnerabilities Vulnerability Assessment Details
|
MailEnable IMAP Server Buffer Overflow and Directory Traversal Vulnerabilities |
||
|
Checks for buffer overflow and directory traversal vulnerabilities in MailEnable IMAP server Detailed Explanation for this Vulnerability Assessment Summary : The remote IMAP server is affected by buffer overflow and directory traversal vulnerabilities. Description : The remote host is running MailEnable, a commercial mail server for Windows. The IMAP server bundled with the version of MailEnable Professional or Enterprise Edition installed on the remote host is prone to a stack-based buffer overflow when handling an overly-long mailbox name in certain commands. An authenticated attacker may be able to leverage this issue to execute arbitrary code remotely as the SYSTEM user. It also fails to filter directory traversal sequences from mailbox names passed to the 'CREATE' and 'RENAME' commands. An authenticated attacker can exploit these issues to create arbitrary directories on the affected host and to cause a denial of service by renaming the mail directories of other users. See also : http://secunia.com/secunia_research/2005-59/advisory/ http://www.mailenable.com/hotfix/ Solution : Upgrade to MailEnable Professional 1.7 or later. Or apply ME-100008, the IMAP Cumulative Hotfix dated November 18th, 2005, referenced in the vendor URL above. Network Security Threat Level: High / CVSS Base Score : 7.0 (AV:R/AC:L/Au:NR/C:P/I:P/A:P/B:N) Networks Security ID: 15492, 15494 Vulnerability Assessment Copyright: This script is Copyright (C) 2005-2006 Tenable Network Security |
||
|
Cables, Connectors |

Kingston 32GB 64GB 128GB 256GB USB 3.0 Flash Drive Thumb Memory Stick Pen lot
$285.90
SanDisk Ultra Luxe USB 3.1 Flash Drive – 5 Pack | Premium Metal USB Flash Drives
$59.99
1/ 10/ 100pcs USB 2.0 2GB, 4GB ,8GB ,16GB ,32GB ,64GB 128GB USB Flash Drives Lot
$269.10
Microsoft Windows 11 Pro 64bit - New Sealed – Flash USB 1 PC
$49.99
USB 3.0 Flash Drive 32GB 64GB 128GB Memory Stick Thumb Stick Lot Pack
$826.09
USB Type-A Flash Drive Metal Memory Stick High Speed USB Drive 128GB 256GB 512GB
$8.47
Wholesale 5/10/100PCS 1MB- 64GB USB 2.0 Flash Drive Memory Stick Jump Drive Lot
$280.00
LOT 10x SanDisk 32GB ULTRA USB 3.0 flash drive SDCZ48-032G 32 GB read 100 MB/s
$39.80
2021 Full Version Office Professional Plus for 1 PC Flash USB Drive
$59.99
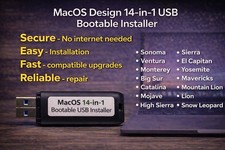
128GB USB 14-in-1 MacOS bootable Installer repair recovery tech support service
$39.99
|
||
|
No Discussions have been posted on this vulnerability. |