|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2007:048: php Vulnerability Assessment Details
|
MDKSA-2007:048: php |
||
|
Check for the version of the php package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2007:048 (php). A number of vulnerabilities were discovered in PHP language. Many buffer overflow flaws were discovered in the PHP session extension, the str_replace() function, and the imap_mail_compose() function. A possible hacker able to use a PHP application using any of these functions could trigger these flaws and possibly execute arbitrary code as the apache user (CVE-2007-0906). A one-byte memory read will always occur prior to the beginning of a buffer, which could be triggered, for example, by any use of the header() function in a script (CVE-2007-0907). The wddx extension, if used to import WDDX data from an untrusted source, may permit a random portion of heap memory to be exposed due to certain WDDX input packets (CVE-2007-0908). The odbc_result_all() function, if used to display data from a database, and if the contents of the database are under the control of an attacker, could lead to the execution of arbitrary code due to a format string vulnerability (CVE-2007-0909). Several flaws in the PHP could permit attackers to clobber certain super-global variables via unspecified vectors (CVE-2007-0910). The zend_hash_init() function can be forced into an infinite loop if unserializing untrusted data on a 64-bit platform, resulting in the consumption of CPU resources until the script timeout alarm aborts the execution of the script (CVE-2007-0988). Updated package have been patched to correct this issue. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2007:048 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

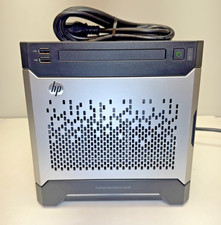
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
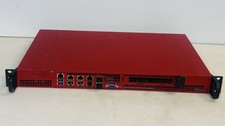
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
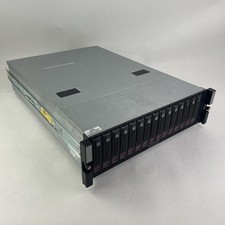
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
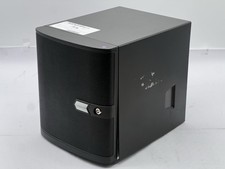
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
Supermicro 1027GR-TSF 1U Rackmount Server 2x Xeon 2.3GHz 128GB DDR3
$219.99
$280.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |