|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2006:197: kernel Vulnerability Assessment Details
|
MDKSA-2006:197: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2006:197 (kernel). Some vulnerabilities were discovered and corrected in the Linux 2.6 kernel: Bugs in the netfilter for IPv6 code, as reported by Mark Dowd, were fixed (CVE-2006-4572). The ATM subsystem of the Linux kernel could permit a remote attacker to cause a Denial of Service (panic) via unknown vectors that cause the ATM subsystem to access the memory of socket buffers after they are freed (CVE-2006-4997). The provided packages are patched to fix these vulnerabilities. All users are encouraged to upgrade to these updated kernels immediately and reboot to effect the fixes. In addition to these security fixes, other fixes have been included such as: - updated to 2.6.17.14 - fix wrong error handling in pccard_store_cis - add NX mask for PTE entry on x86_64 - fix snd-hda-intel OOPS - backported support r8169-related (r8168/r8169SC) network chipsets - explicitly initialize some members of the drm_driver structure, otherwise NULL init will have bad side effects (mach64) - support for building a nosrc.rpm package - fixed unplug/eject on pcmcia cards with r8169 chipsets - fix libata resource conflicts - fix xenU crash and re-enable domU boot logs - fix refcount error triggered by software using /proc/[pid]/auxv To update your kernel, please follow the directions located at: http://www.mandriva.com/en/security/kernelupdate Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2006:197 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

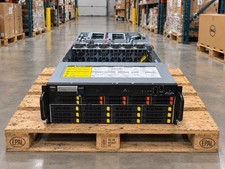
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99
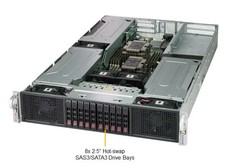
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99
|
||
|
No Discussions have been posted on this vulnerability. |