|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2006:185: php Vulnerability Assessment Details
|
MDKSA-2006:185: php |
||
|
Check for the version of the php package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2006:185 (php). PHP 4.x up to 4.4.4 and PHP 5 up to 5.1.6 permits local users to bypass certain Apache HTTP Server httpd.conf options, such as safe_mode and open_basedir, via the ini_restore function, which resets the values to their php.ini (Master Value) defaults. (CVE-2006-4625) A race condition in the symlink function in PHP 5.1.6 and earlier permits local users to bypass the open_basedir restriction by using a combination of symlink, mkdir, and unlink functions to change the file path after the open_basedir check and before the file is opened by the underlying system, as demonstrated by symlinking a symlink into a subdirectory, to point to a parent directory via .. (dot dot) sequences, and then unlinking the resulting symlink. (CVE-2006-5178) Because the design flaw cannot be solved it is strongly recommended to disable the symlink() function if you are using the open_basedir feature. You can achieve that by adding symlink to the list of disabled functions within your php.ini: disable_functions=...,symlink The updated packages do not alter the system php.ini. Updated packages have been patched to correct the CVE-2006-4625 issue. Users must restart Apache for the changes to take effect. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2006:185 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

Vintage DEC E2052-AA AlphaServer I/O Board 9 Gold Ceramic ICs 4.3 LB Gold Scrap
$729.99
Vintage DEC Digital T1043 DWMBB/B VAXBI XMI Adapter 5018232-01 C1 VAX Board
$109.99
Vintage DEC Digital XMI-A1 5017293-01A1 LWPR BE3-0 VAX Circuit Board T2012
$74.99
Vintage DEC/Mostek memory systems MK 8015 AA-00 6805-08015 1100 REV C(B7)
$279.99
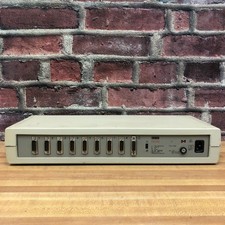
Vintage DEC Digital Equipment DELNI 8-Port Ethernet Local Network Hub VAXstation
$79.95
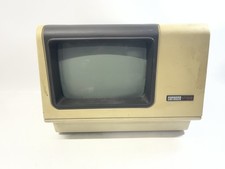
Vintage DEC VT100 Series Terminal (Powers On)
$499.99
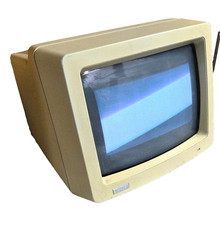
Vintage Digital VR241-A color CRT monitor, powers on, DEC Rainbow or terminal
$150.00
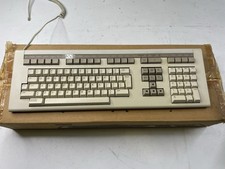
Vintage DEC LK201 Digital Equipment Corporation (DEC) LK201-AA Computer Keyboard
$149.99
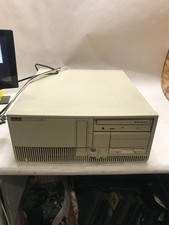
Vintage DEC Digital Starion 200 Desktop PC Powers On Boots To BIOS NO HDD - DW
$269.99
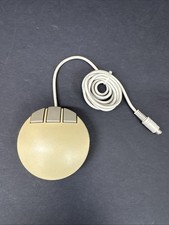
Vintage DEC Digital VSXXX-AA.B03 Hawley 3-Button Mouse 1986 Tested Working
$111.00
|
||
|
No Discussions have been posted on this vulnerability. |