|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2006:159: sudo Vulnerability Assessment Details
|
MDKSA-2006:159: sudo |
||
|
Check for the version of the sudo package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2006:159 (sudo). Previous sudo updates were made available to sanitize certain environment variables from affecting a sudo call, such as PYTHONINSPECT, PERL5OPT, etc. While those updates were effective in addressing those specific environment variables, other variables that were not blacklisted were being made available. Debian addressed this issue by forcing sudo to use a whitlist approach in DSA-946-2 by arbitrarily making env_reset the default (as opposed to having to be enabled in /etc/sudoers). Mandriva has opted to follow the same approach so now only certain variables are, by default, made available, such as HOME, LOGNAME, SHELL, TERM, DISPLAY, XAUTHORITY, XAUTHORIZATION, LANG, LANGUAGE, LC_*, and USER, as well as the SUDO_* variables. If other variables are required to be kept, this can be done by editing /etc/sudoers and using the env_keep option, such as: Defaults env_keep='FOO BAR' As well, the Corporate 3 packages are now compiled with the SECURE_PATH setting. Updated packages are patched to address this issue. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2006:159 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

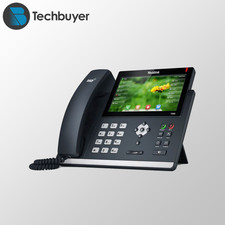
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
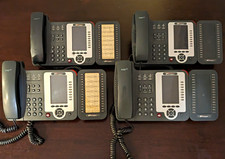
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
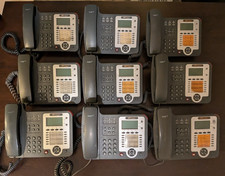
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
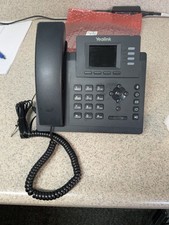
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
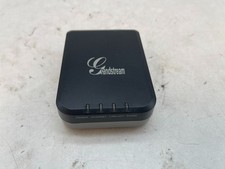
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
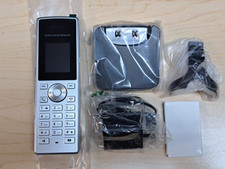
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28

Cisco / Linksys SPA2102 VoIP 2FXS Phone Adapter with Router (unlocked)
$18.99
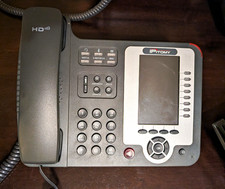
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
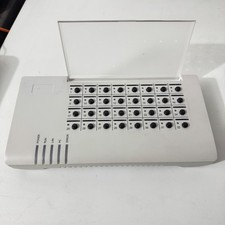
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |