|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2006:010: cups Vulnerability Assessment Details
|
MDKSA-2006:010: cups |
||
|
Check for the version of the cups package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2006:010 (cups). Multiple heap-based buffer overflows in the DCTStream::readProgressiveSOF and DCTStream::readBaselineSOF functions in the DCT stream parsing code (Stream.cc) in xpdf 3.01 and earlier, permit user-complicit attackers to cause a denial of service (heap corruption) and possibly execute arbitrary code via a crafted PDF file with an out-of-range number of components (numComps), which is used as an array index. (CVE-2005-3191) Heap-based buffer overflow in the StreamPredictor function in Xpdf 3.01 permits remote attackers to execute arbitrary code via a PDF file with an out-of-range numComps (number of components) field. (CVE-2005-3192) Heap-based buffer overflow in the JPXStream::readCodestream function in the JPX stream parsing code (JPXStream.c) for xpdf 3.01 and earlier permits user-complicit attackers to cause a denial of service (heap corruption) and possibly execute arbitrary code via a crafted PDF file with large size values that cause insufficient memory to be allocated. (CVE-2005-3193) An additional patch re-addresses memory allocation routines in goo/gmem.c (Martin Pitt/Canonical, Dirk Mueller/KDE). In addition, Chris Evans discovered several other vulnerbilities in the xpdf code base: Out-of-bounds heap accesses with large or negative parameters to 'FlateDecode' stream. (CVE-2005-3192) Out-of-bounds heap accesses with large or negative parameters to 'CCITTFaxDecode' stream. (CVE-2005-3624) Infinite CPU spins in various places when stream ends unexpectedly. (CVE-2005-3625) NULL pointer crash in the 'FlateDecode' stream. (CVE-2005-3626) Overflows of compInfo array in 'DCTDecode' stream. (CVE-2005-3627) Possible to use index past end of array in 'DCTDecode' stream. (CVE-2005-3627) Possible out-of-bounds indexing trouble in 'DCTDecode' stream. (CVE-2005-3627) CUPS uses an embedded copy of the xpdf code, with the same vulnerabilities. The updated packages have been patched to correct these problems. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2006:010 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

RAM-HOL-SAM60CPU RAM USB-C Powered Dock for Samsung Tab Active5 - 3 - 2
$81.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Samsung Chromebook 11.6" Intel Celeron Chrome OS Gray (Charger Inc)
$22.00
RAM-GDS-SKIN-SAM54-NG-1 RAM Mounts IntelliSkin® Next Gen for Samsung Tab Active4
$93.99
RAM-HOL-SAM52CPU RAM USB-C Powered Dock Samsung Tab Active4 Pro & Tab Active Pro
$81.99
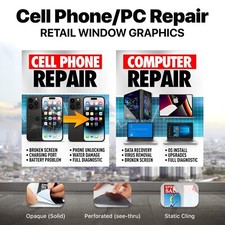
Cell Phone Smartphone Computer repair banner poster sign iphone Samsung
$89.99
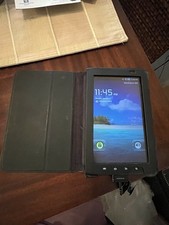
Samsung Galaxy Tab SCH-1800 7" 4GB Wi-Fi + Verizon Tablet Working
$30.00
Samsung Galaxy View Tablet 18.4 SM-T670/677A Charging Port 100% Original Oem
$98.99
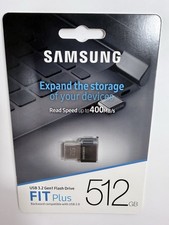
New Samsung 512GB FIT Plus USB 3.2 Gen 1 Type-A Flash Drive MUF-512AB/AM NEW
$120.00
|
||
|
No Discussions have been posted on this vulnerability. |