|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2005:186-1: lynx Vulnerability Assessment Details
|
MDKSA-2005:186-1: lynx |
||
|
Check for the version of the lynx package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2005:186-1 (lynx). Ulf Harnhammar discovered a remote buffer overflow in lynx versions 2.8.2 through 2.8.5. When Lynx connects to an NNTP server to fetch information about the available articles in a newsgroup, it will call a function called HTrjis() with the information from certain article headers. The function adds missing ESC characters to certain data, to support Asian character sets. However, it does not check if it writes outside of the char array buf, and that causes a remote stack-based buffer overflow, with full control over EIP, EBX, EBP, ESI and EDI. Two attack vectors to make a victim visit a URL to a dangerous news server are: (a) *redirecting scripts*, where the victim visits some web page and it redirects automatically to a malicious URL, and (b) *links in web pages*, where the victim visits some web page and selects a link on the page to a malicious URL. Attack vector (b) is helped by the fact that Lynx does not automatically display where links lead to, unlike many graphical web browsers. The updated packages have been patched to address this issue. Update: The previous patchset had a bug in the patches themselves, which was uncovered by Klaus Singvogel of Novell/SUSE in auditing crashes on some architectures. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2005:186-1 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
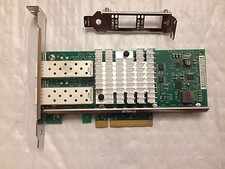
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
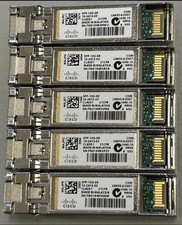
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |