|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2005:179: openssl Vulnerability Assessment Details
|
MDKSA-2005:179: openssl |
||
|
Check for the version of the openssl package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2005:179 (openssl). Yutaka Oiwa discovered vulnerability potentially affects applications that use the SSL/TLS server implementation provided by OpenSSL. Such applications are affected if they use the option SSL_OP_MSIE_SSLV2_RSA_PADDING. This option is implied by use of SSL_OP_ALL, which is intended to work around various bugs in third- party software that might prevent interoperability. The SSL_OP_MSIE_SSLV2_RSA_PADDING option disables a verification step in the SSL 2.0 server supposed to prevent active protocol-version rollback attacks. With this verification step disabled, an attacker acting as a 'man in the middle' can force a client and a server to negotiate the SSL 2.0 protocol even if these parties both support SSL 3.0 or TLS 1.0. The SSL 2.0 protocol is known to have severe cryptographic weaknesses and is supported as a fallback only. (CVE-2005-2969) The current default algorithm for creating 'message digests' (electronic signatures) for certificates created by openssl is MD5. However, this algorithm is not deemed secure any more, and some practical attacks have been demonstrated which could permit a possible hacker to forge certificates with a valid certification authority signature even if he does not know the secret CA signing key. To address this issue, openssl has been changed to use SHA-1 by default. This is a more appropriate default algorithm for the majority of use cases. If you still want to use MD5 as default, you can revert this change by changing the two instances of 'default_md = sha1' to 'default_md = md5' in /usr/{lib,lib64}/ ssl/openssl.cnf. (CVE-2005-2946) Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2005:179 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

(New) AMD Ryzen 7 5700X 8 Core 16 Thread AM4 Unlocked 3.4 GHz CPU OEM Tray
$174.99
Microsoft Surface Pro 5 Silver 128GB SSD 4gb RAM
$97.97
SGIN 17.3" Laptop Intel Quad-Core Up to 2.4 GHZ 8GB RAM 256GB SSD HD
$229.99
Lenovo IdeaPad S340-15IWL Laptop 15.6" Intel Core i3-8145U 8GB RAM 256GB SSD
$126.65
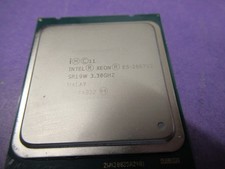
Intel Xeon E5 - 2667V2 / SR19W 3.30GHz 25MB 8-Core CPU Socket LGA2011
$30.00

AMD FX 8350 8-CORE 4.00GHz CPU FD8350FRW8KHK SOCKET AM3+ *QTY
$39.99
AMD Ryzen 7 7800X3D 4.20GHz Quad Core 100-000000510 8 Thread AM4
$279.99
AMD Ryzen 7 5700G 8-Core 16-Thread 4.6GHz Max Boost, 3.8 GHz Base
$170.00
$600.00
Dell T7810 Workstation 8-Core 2.40GHz E5-2630 v3 No RAM GPU HDD OS
$259.98
|
||
|
No Discussions have been posted on this vulnerability. |