|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2005:170: mozilla Vulnerability Assessment Details
|
MDKSA-2005:170: mozilla |
||
|
Check for the version of the mozilla package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2005:170 (mozilla). A number of vulnerabilities have been discovered in Mozilla that have been corrected in version 1.7.12: A bug in the way Mozilla processes XBM images could be used to execute arbitrary code via a specially crafted XBM image file (CVE-2005-2701). A bug in the way Mozilla handles certain Unicode sequences could be used to execute arbitrary code via viewing a specially crafted Unicode sequence (CVE-2005-2702). A bug in the way Mozilla makes XMLHttp requests could be abused by a malicious web page to exploit other proxy or server flaws from the victim's machine however, the default behaviour of the browser is to dispermit this (CVE-2005-2703). A bug in the way Mozilla implemented its XBL interface could be abused by a malicious web page to create an XBL binding in such a way as to permit arbitrary JavaScript execution with chrome permissions (CVE-2005-2704). An integer overflow in Mozilla's JavaScript engine could be manipulated in certain conditions to permit a malicious web page to execute arbitrary code (CVE-2005-2705). A bug in the way Mozilla displays about: pages could be used to execute JavaScript with chrome rights (CVE-2005-2706). A bug in the way Mozilla opens new windows could be used by a malicious web page to construct a new window without any user interface elements (such as address bar and status bar) that could be used to potentially mislead the user (CVE-2005-2707). Tom Ferris reported that Firefox would crash when processing a domain name consisting solely of soft-hyphen characters due to a heap overflow when IDN processing results in an empty string after removing non- wrapping chracters, such as soft-hyphens. This could be exploited to run or or install malware on the user's computer (CVE-2005-2871). The updated packages have been patched to address these issues and all users are urged to upgrade immediately. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2005:170 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

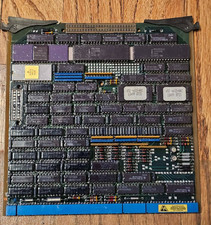
Vintage Intel 8085 CPU Processor Board Ceramic Gold IC Industrial Military Rare
$199.95
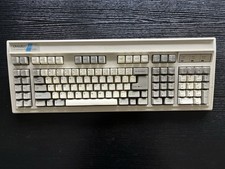
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
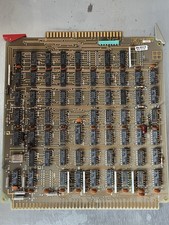
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
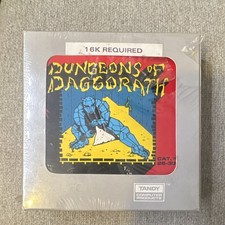
Dungeons of Daggorath TRS-80 Color Computer Tandy 26-3093 SEALED Vintage 1982
$119.99
vintage pentium 3 pc turns on no display no post
$150.00
Original Vintage Old Style STANDARD Black CD Jewel Case (Heavy Duty) 90g Lot
$316.95
New Old Stock Vintage Fujitsu Lifebook P1630 UMPC Laptop Retro Computer
$249.99
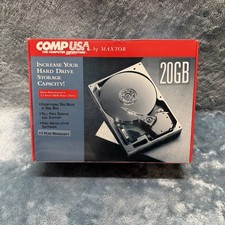
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
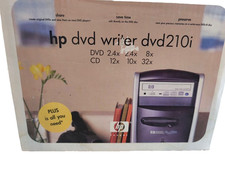
Vintage HP DVD Writer dvd210i Internal IDE Drive Q2116A BRAND NEW FACTORY SEALED
$58.85
|
||
|
No Discussions have been posted on this vulnerability. |