|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2005:119: krb5 Vulnerability Assessment Details
|
MDKSA-2005:119: krb5 |
||
|
Check for the version of the krb5 package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2005:119 (krb5). A number of vulnerabilities have been corrected in this Kerberos update: The rcp protocol would permit a server to instruct a client to write to arbitrary files outside of the current directory. The Kerberos-aware rcp could be abused to copy files from a malicious server (CVE-2004-0175). Gael Delalleau discovered an information disclosure vulnerability in the way some telnet clients handled messages from a server. This could be abused by a malicious telnet server to collect information from the environment of any victim connecting to the server using the Kerberos- aware telnet client (CVE-2005-0488). Daniel Wachdorf disovered that in error conditions that could occur in response to correctly-formatted client requests, the Kerberos 5 KDC may attempt to free uninitialized memory, which could cause the KDC to crash resulting in a Denial of Service (CVE-2005-1174). Daniel Wachdorf also discovered a single-byte heap overflow in the krb5_unparse_name() function that could, if successfully exploited, lead to a crash, resulting in a DoS. To trigger this flaw, a possible hacker would need to have control of a Kerberos realm that shares a cross- realm key with the target (CVE-2005-1175). Finally, a double-free flaw was discovered in the krb5_recvauth() routine which could be triggered by a remote unauthenticated attacker. This issue could potentially be exploited to permit for the execution of arbitrary code on a KDC. No exploit is currently known to exist (CVE-2005-1689). The updated packages have been patched to address this issue and Mandriva urges all users to upgrade to these packages as quickly as possible. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2005:119 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |


Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$549.00
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
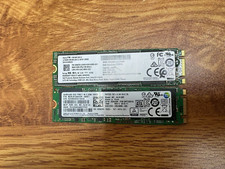
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
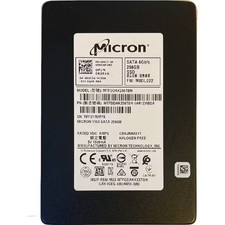
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
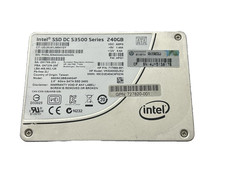
Intel Solid-State Drive DC S3500 Series 240GB Internal 2.5" (SSDSC2BB240G4P) SSD
$29.99
|
||
|
No Discussions have been posted on this vulnerability. |