|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2005:072: php Vulnerability Assessment Details
|
MDKSA-2005:072: php |
||
|
Check for the version of the php package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2005:072 (php). A number of vulnerabilities are addressed in this PHP update: Stefano Di Paolo discovered integer overflows in PHP's pack(), unpack(), and shmop_write() functions which could permit a malicious script to break out of safe mode and execute arbitray code with rights of the PHP interpreter (CVE-2004-1018 this was previously fixed in Mandrakelinux >= 10.0 in MDKSA-2004:151). Stefan Esser discovered two safe mode bypasses which would permit malicious scripts to circumvent path restrictions by using virtual_popen() with a current directory containing shell meta- characters (CVE-2004-1063) or by creating a specially crafted directory whose length exceeded the capacity of realpath() (CVE-2004-1064 both of these were previously fixed in Mandrakelinux >= 10.0 in MDKSA-2004:151). Two Denial of Service vulnerabilities were found in the getimagesize() function which uses the format-specific internal functions php_handle_iff() and php_handle_jpeg() which would get stuck in infinite loops when certain (invalid) size parameters are read from the image (CVE-2005-0524 and CVE-2005-0525). An integer overflow was discovered in the exif_process_IFD_TAG() function in PHP's EXIF module. EXIF tags with a specially crafted 'Image File Directory' (IFD) tag would cause a buffer overflow which could be exploited to execute arbitrary code with the rights of the PHP server (CVE-2005-1042). Another vulnerability in the EXIF module was also discovered where headers with a large IFD nesting level would cause an unbound recursion which would eventually overflow the stack and cause the executed program to crash (CVE-2004-1043). All of these issues are addressed in the Corporate Server 2.1 packages and the last three issues for all other platforms, which had previously included the first two issues but had not been mentioned in MDKSA-2004:151. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2005:072 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |


Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$379.00

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
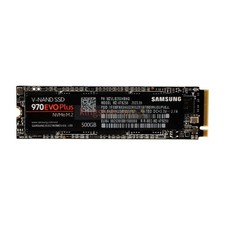
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99
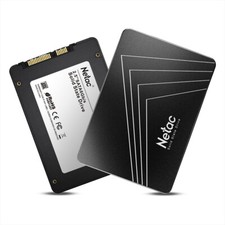
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00

Netac 256GB SSD 2.5'' SATA III 6Gb/s Internal Solid State Drive 500MB/s PC/Latop
$40.00
|
||
|
No Discussions have been posted on this vulnerability. |