|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2004:151: php Vulnerability Assessment Details
|
MDKSA-2004:151: php |
||
|
Check for the version of the php package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2004:151 (php). A number of vulnerabilities in PHP versions prior to 4.3.10 were discovered by Stefan Esser. Some of these vulnerabilities were not deemed to be severe enough to warrant CVE names, however the packages provided, with the exception of the Corporate Server 2.1 packages, include fixes for all of the vulnerabilities, thanks to the efforts of the OpenPKG team who extracted and backported the fixes. The vulnerabilities fixed in all provided packages include a fix for a possible information disclosure, double free, and negative reference index array underflow in deserialization code (CVE-2004-1019). As well, the exif_read_data () function suffers from an overflow on a long sectionname this vulnerability was discovered by Ilia Alshanetsky (CVE-2004-1065). The other fixes that appear in Mandrakelinux 9.2 and newer packages include a fix for out of bounds memory write access in shmop_write() and integer overflow /underflows in the pack() and unpack() functions. The addslashes() function did not properly escape ' Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2004:151 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

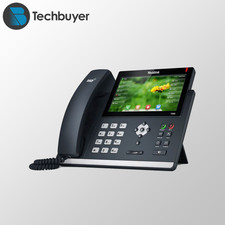
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
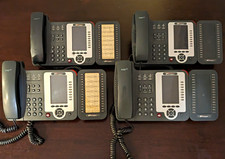
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
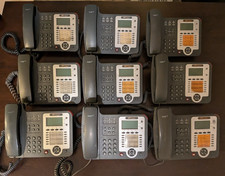
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
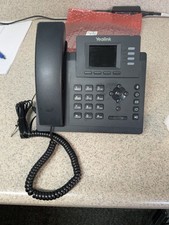
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
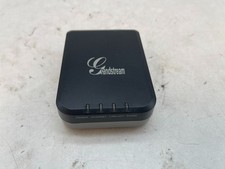
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
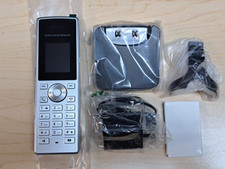
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28

Cisco / Linksys SPA2102 VoIP 2FXS Phone Adapter with Router (unlocked)
$18.99
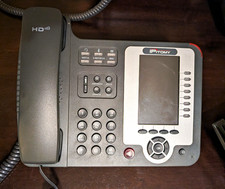
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
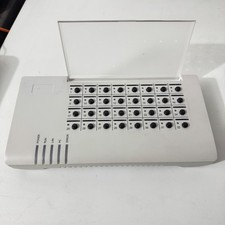
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |