|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2004:150: kdelibs Vulnerability Assessment Details
|
MDKSA-2004:150: kdelibs |
||
|
Check for the version of the kdelibs package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2004:150 (kdelibs). Daniel Fabian discovered a potential privacy issue in KDE. When creating a link to a remote file from various applications, including Konqueror, the resulting URL may contain the authentication credentials used to access that remote resource. This includes, but is not limited to, browsing SMB (Samba) shares. Upon further investigation, it was found that the SMB protocol handler also unnecessarily exposed authentication credentials (CVE-2004-1171). Another vulnerability was discovered where a malicious website could abuse Konqueror to load its own content into a window or tab that was opened by a trusted website, or it could trick a trusted website into loading content into an existing window or tab. This could lead to the user being confused as to the origin of a particular webpage and could have the user unknowingly send confidential information intended for a trusted site to the malicious site (CVE-2004-1158). The updated packages contain a patch from the KDE team to solve this issue. Additionally, the kdelibs and kdebase packages for Mandrakelinux 10.1 contain numerous bugfixes. New qt3 packages are being provided for Mandrakelinux 10.0 that are required to build the kdebase package. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2004:150 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

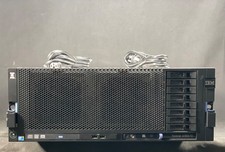
IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
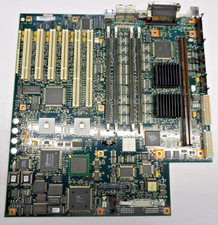
Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$179.99
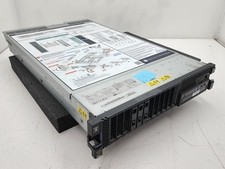
IBM Power 8 S822L Server 8247-22L POWER8 Enterprise 256GB RAM 2x 00KV626 CPU
$999.99
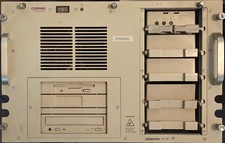
Compaq ProLiant 1500R 5/100 rack server, Series 3155, with IBM 2.1GB HD, VINTAGE
$295.00
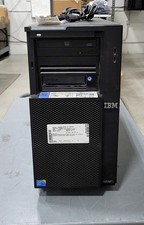
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$110.30
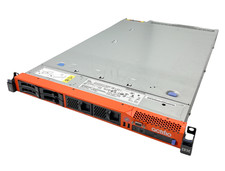
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$150.00
Rare Vintage IBM 93ZZ PowerPC Server Board - MCM Ceramic CPU - 40N1844 - 1.1 lbs
$49.99
DELL POWEREDGE HP IBM SERVER XEON GOLD 5315Y 8 CORE PROCESSOR 3.2 GHZ SRKXR
$1100.00
|
||
|
No Discussions have been posted on this vulnerability. |