|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2004:086: kdelibs/kdebase Vulnerability Assessment Details
|
MDKSA-2004:086: kdelibs/kdebase |
||
|
Check for the version of the kdelibs/kdebase package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2004:086 (kdelibs/kdebase). A number of vulnerabilities were discovered in KDE that are corrected with these update packages. The integrity of symlinks used by KDE are not ensured and as a result can be abused by local attackers to create or truncate arbitrary files or to prevent KDE applications from functioning correctly (CVE-2004-0689). The DCOPServer creates temporary files in an insecure manner. These temporary files are used for authentication-related purposes, so this could potentially permit a local attacker to compromise the account of any user running a KDE application (CVE-2004-0690). Note that only KDE 3.2.x is affected by this vulnerability. The Konqueror web browser permits websites to load web pages into a frame of any other frame-based web page that the user may have open. This could potentially permit a malicious website to make Konqueror insert its own frames into the page of an otherwise trusted website (CVE-2004-0721). The Konqueror web browser also permits websites to set cookies for certain country-specific top-level domains. This can be done to make Konqueror send the cookies to all other web sites operating under the same domain, which can be abused to become part of a session fixation attack. All country-specific secondary top-level domains that use more than 2 characters in the secondary part of the domain name, and that use a secondary part other than com, net, mil, org, gove, edu, or int are affected (CVE-2004-0746). Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2004:086 Network Security Threat Level: High Networks Security ID: 10991, 11186, 11552 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

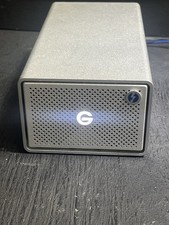
G-Technology G-RAID 24TB Dual-Drive External HDD TB3 USB 3.1 7200RPM Silver
$299.99

OWC Mercury Elite Pro 2 Bay RAID Enclosure with USB 3.2 for Dual 3.5 inch HDDs
$87.99
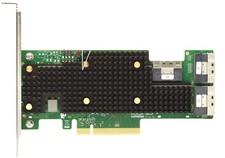
Broadcom 9600-24i RAID Controller PCIe Gen 4.1 Tri-Mode NEW 05-50111-01004
$649.99
Intel VROC Premium RAID Controller Card PCIe Add-On Module VROCPREMMOD
$265.00
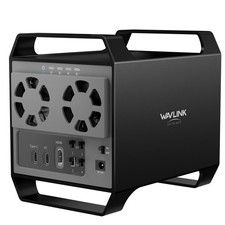
2-Bay/4-Bay Hard Drive Enclosure for 3.5"/2.5'' SATA HDD/SSD 10Gbps USB-C 3.2
$75.99
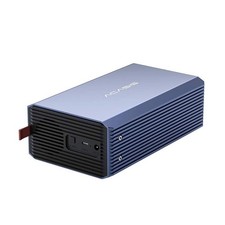
Acasis USB 3.2 2 Bay HDD RAID Enclosure for 2.5/3.5" SATA Drives External Array
$55.00
MegaRAID 9580-8i8e 16-port 12G SAS/SATA/NVMe 8GB PCIe RAID - 05-50076-00
$1619.19
Dell PowerEdge HBA330 LP PCI-E 12GBs RAID SAS Controller Adapter J7TNV
$18.95
Broadcom MegaRAID 9480-8e Fujitsu PRAID EP540e SAS RAID Card (Replac 9380-8e) 8i
$228.00
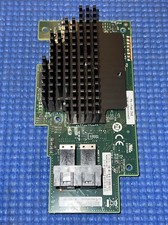
Intel® Integrated RAID Mezzanine Module RMS3HC080 SAS/SATA H24093-204
$24.97
|
||
|
No Discussions have been posted on this vulnerability. |