|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2004:071: samba Vulnerability Assessment Details
|
MDKSA-2004:071: samba |
||
|
Check for the version of the samba package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2004:071 (samba). A vulnerability was discovered in SWAT, the Samba Web Administration Tool. The routine used to decode the base64 data during HTTP basic authentication is subject to a buffer overrun caused by an invalid base64 character. This same code is also used to internally decode the sambaMungedDial attribute value when using the ldapsam passdb backend, and to decode input given to the ntlm_auth tool. This vulnerability only exists in Samba versions 3.0.2 or later the 3.0.5 release fixes the vulnerability. Systems using SWAT, the ldapsam passdb backend, and tose running winbindd and permiting third- party applications to issue authentication requests via ntlm_auth tool should upgrade immediately. (CVE-2004-0600) A buffer overrun has been located in the code used to support the 'mangling method = hash' smb.conf option. Please be aware that the default setting for this parameter is 'mangling method = hash2' and therefore not vulnerable. This bug is present in Samba 3.0.0 and later, as well as Samba 2.2.X (CVE-2004-0686) This update also fixes a bug where attempting to print in some cases would cause smbd to exit with a signal 11. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2004:071 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

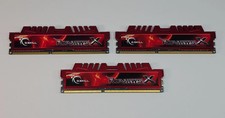
16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
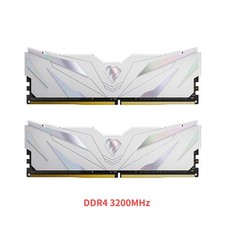
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
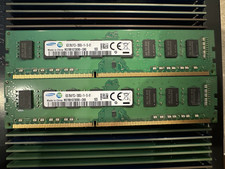
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
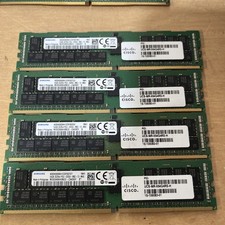
Samsung 64GB PC4-2666V-R 2S2Rx4 DDR4 ECC REG RDIMM - M393A8K40B22-CWD6Y
$270.00
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
Lot 500 SK hynix 16GB 2Rx8 PC4-23400 DDR4-2933Y ECC Registered Server Memory RAM
$47988.00
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
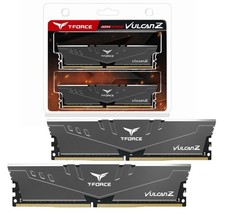
TeamGroup T-FORCE VULCAN Z 16GB (2 x 8GB) DDR4 3000Mz (PC4 24000) Desktop Memory
$97.76
|
||
|
No Discussions have been posted on this vulnerability. |