|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2003:109: gnupg Vulnerability Assessment Details
|
MDKSA-2003:109: gnupg |
||
|
Check for the version of the gnupg package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2003:109 (gnupg). A severe vulnerability was discovered in GnuPG by Phong Nguyen relating to ElGamal sign+encrypt keys. From Werner Koch's email message: 'Phong Nguyen identified a severe bug in the way GnuPG creates and uses ElGamal keys for signing. This is a significant security failure which can lead to a compromise of almost all ElGamal keys used for signing. Note that this is a real world vulnerability which will reveal your private key within a few seconds. Please *take immediate action and revoke your ElGamal signing keys*. Furthermore you should take whatever measures necessary to limit the damage done for signed or encrypted documents using that key.' And also: 'Note that the standard keys as generated by GnuPG (DSA and ElGamal encryption) as well as RSA keys are NOT vulnerable. Note also that ElGamal signing keys cannot be generated without the use of a special flag to enable hidden options and even then overriding a warning message about this key type. See below for details on how to identify vulnerable keys.' MandrakeSoft urges any users who use the ElGamal sign+encrypt keys to immediately revoke these keys and discontinue use of them. Updated packages are provided that remove the ability to create these keys and to create signatures using these keys (thanks to David Shaw for writing the patch). Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2003:109 Network Security Threat Level: High Networks Security ID: 9115 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

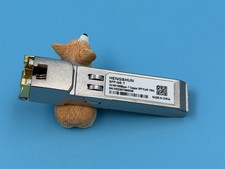
SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
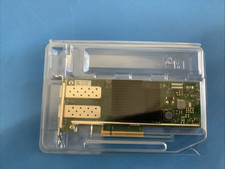
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
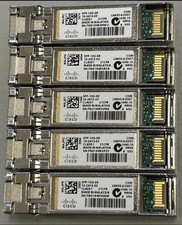
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
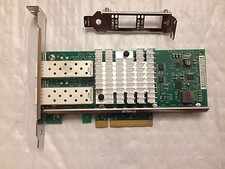
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99
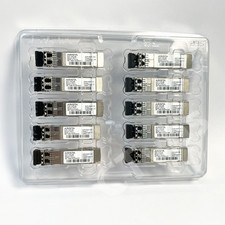
Lot of 10 ARISTA SFP-10G-SR 10GBASE-SR SFP LC Connector Optic Transceiver Module
$60.72
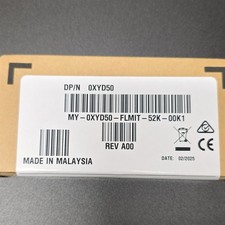
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |