|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2003:075-1: apache2 Vulnerability Assessment Details
|
MDKSA-2003:075-1: apache2 |
||
|
Check for the version of the apache2 package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2003:075-1 (apache2). Several vulnerabilities were discovered in Apache 2.x versions prior to 2.0.47. From the Apache 2.0.47 release notes: Certain sequences of per-directory renegotiations and the SSLCipherSuite directive being used to upgrade from a weak ciphersuite to a strong one could result in the weak ciphersuite being used in place of the new one (CVE-2003-0192). Certain errors returned by accept() on rarely accessed ports could cause temporary Denial of Service due to a bug in the prefork MPM (CVE-2003-0253). Denial of Service was caused when target host is IPv6 but FTP proxy server can't create IPv6 socket (CVE-2003-0254). The server would crash when going into an infinite loop due to too many subsequent internal redirects and nested subrequests (VU#379828). The Apache Software Foundation thanks Saheed Akhtar and Yoshioka Tsuneo for responsibly reporting these issues. To upgrade these apache packages, first stop Apache by issuing, as root: service httpd stop After the upgrade, restart Apache with: service httpd start Update: The previously released packages had a manpage conflict between apache2-common and apache-1.3 that prevented both packages from being installed at the same time. This update provides a fixed apache2-common package. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2003:075-1 Network Security Threat Level: High Networks Security ID: 8134, 8135, 8137 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

Apple Macintosh Plus 1MB M0001A Vintage Computer Boots Up / Floppy Disk Stuck
$99.99
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
Vintage 1998 iMac G3 M4984 Mac OS + Keyboard Working but Needs Some Repair Read
$295.00
Apple Power Macintosh PowerPC 7300/200 VTG w Keyboard Mouse Storage Drive Read
$199.99
Macintosh MacTerminal M0521 Version 1.0. Vintage Apple software 1984 Sealed
$129.99
Vintage 1992 Mac System 7.1P1 Apple Software 3.5” Floppy Disks NOS
$35.00
185--Sonnet Crescendo G3 PPCG3-375-5-K-06 G3 Add-On Card for Vintage Mac
$90.00
Apple Macintosh Plus 1MB M0001A Vintage Computer - Works
$169.99
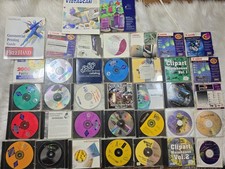
Mixed Lot Vintage Mac Windows media / Graphics / Sound Software - CDs 37 Pieces
$40.99
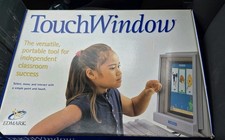
Vintage Edmark TouchWindow for Macintosh DeskTop Computer Touch Window Never Usd
$63.99
|
||
|
No Discussions have been posted on this vulnerability. |