|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2003:039: kernel22 Vulnerability Assessment Details
|
MDKSA-2003:039: kernel22 |
||
|
Check for the version of the kernel22 package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2003:039 (kernel22). A number of vulnerabilities have been found in the Linux 2.2 kernel that have been addressed with the latest 2.2.25 release. A bug in the kernel module loader code could permit a local user to gain root rights. This is done by a local user using ptrace and attaching to a modprobe process that is spawned if the user triggers the loading of a kernel module. A temporary workaround can be used to defend against this flaw. It is possible to temporarily disable the kmod kernel module loading subsystem in the kernel after all of the required kernel modules have been loaded. Be sure that you do not need to load additional kernel modules after implementing this workaround. To use it, as root execute: echo /no/such/file >/proc/sys/kernel/modprobe To automate this, you may wish to add it as the last line of the /etc/rc.d/rc.local file. You can revert this change by replacing the content '/sbin/modprobe' in the /proc/sys/kernel/modprobe file. The root user can still manually load kernel modules with this workaround in place. As well, multiple ethernet device drivers do not pad frames with null bytes, which could permit remote attackers to obtain information from previous packets or kernel memory by using malformed packets. Finally, the 2.2 kernel permits local users to cause a crash of the host system by using the mmap() function with a PROT_READ parameter to access non-readable memory pages through the /proc/pid/mem interface. All users are encouraged to upgrade to the latest kernel version provided. For instructions on how to upgrade your kernel in Mandrake Linux, please refer to: http://www.mandrakesecure.net/en/kernelupdate.php Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2003:039 Network Security Threat Level: High Networks Security ID: 6420 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
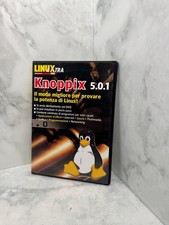
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |