|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2003:001: cups Vulnerability Assessment Details
|
MDKSA-2003:001: cups |
||
|
Check for the version of the cups package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2003:001 (cups). iDefense reported several security problems in CUPS that can lead to local and remote root compromise. An integer overflow in the HTTP interface can be used to gain remote access with CUPS privilege. A local file race condition can be used to gain root privilege, although the previous bug must be exploited first. An attacker can remotely add printers to the vulnerable system. A remote DoS can be accomplished due to negative length in the memcpy() call. An integer overflow in image handling code can be used to gain higher privilege. A possible hacker can gain local root privilege due to a buffer overflow of the 'options' buffer. A design problem can be exploited to gain local root access, however this needs an added printer (which can also be done, as per a previously noted bug). Wrong handling of zero-width images can be abused to gain higher privilege. Finally, a file descriptor leak and DoS due to missing checks of return values of file/socket operations. MandrakeSoft recommends all users upgrade these CUPS packages immediately. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2003:001 Network Security Threat Level: High Networks Security ID: 6433, 6434, 6435, 6436, 6437, 6438, 6439, 6440, 6475 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

Apple Macintosh Plus 1MB M0001A Vintage Computer Boots Up / Floppy Disk Stuck
$99.99
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
Vintage 1998 iMac G3 M4984 Mac OS + Keyboard Working but Needs Some Repair Read
$295.00
Apple Power Macintosh PowerPC 7300/200 VTG w Keyboard Mouse Storage Drive Read
$199.99
185--Sonnet Crescendo G3 PPCG3-375-5-K-06 G3 Add-On Card for Vintage Mac
$90.00
Vintage 1992 Mac System 7.1P1 Apple Software 3.5” Floppy Disks NOS
$35.00
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
Macintosh MacTerminal M0521 Version 1.0. Vintage Apple software 1984 Sealed
$129.99
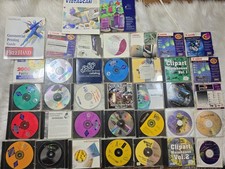
Mixed Lot Vintage Mac Windows media / Graphics / Sound Software - CDs 37 Pieces
$40.99
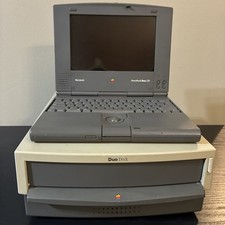
Apple Macintosh DuoDock Duo Dock M7779 & Powerbook 230 Vintage Mac RARE Vintage
$249.00
|
||
|
No Discussions have been posted on this vulnerability. |