|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2002:046-1: openssl Vulnerability Assessment Details
|
MDKSA-2002:046-1: openssl |
||
|
Check for the version of the openssl package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2002:046-1 (openssl). An audit of the OpenSSL code by A.L. Digital Ltd and The Bunker, under the DARPA program CHATS, discovered a number of vulnerabilities in the OpenSSL code that are all potentially remotely exploitable. From the OpenSSL advisory: 1. The client master key in SSL2 could be oversized and overrun a buffer. This vulnerability was also independently discovered by consultants at Neohapsis (http://www.neohapsis.com/) who have also demonstrated that the vulerability is exploitable. Exploit code is NOT available at this time. 2. The session ID supplied to a client in SSL3 could be oversized and overrun a buffer. 3. The master key supplied to an SSL3 server could be oversized and overrun a stack-based buffer. This issues only affects OpenSSL 0.9.7 with Kerberos enabled. 4. Various buffers for ASCII representations of integers were too small on 64 bit platforms. At the same time, various potential buffer overflows have had assertions added these are not known to be exploitable. Finally, a vulnerability was found by Adi Stav and James Yonan independantly in the ASN1 parser which can be confused by supplying it with certain invalid encodings. There are no known exploits for this vulnerability. All of these vulnerabilities are fixed in OpenSSL 0.9.6f. Patches have been applied to the versions of OpenSSL provided in this update to fix all of these problems, except for the ASN1 vulnerability, which a fix will be provided for once MandrakeSoft has had a chance to QA the new packages. In the meantime, it is is strongly encouraged that all users upgrade to these OpenSSL packages. Update: These new OpenSSL packages are available to additionally fix the ASN1 vulnerability described above. All Mandrake Linux users are encouraged to upgrade to these new packages. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2002:046-1 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
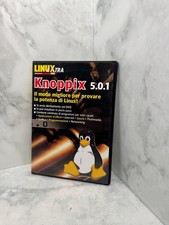
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |