|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2002:039-2: apache Vulnerability Assessment Details
|
MDKSA-2002:039-2: apache |
||
|
Check for the version of the apache package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2002:039-2 (apache). [ Please note that this advisory supersedes the previous MDKSA-2002:039 and MDKSA-2002:039-1 advisories. ] MandrakeSoft is urging all users of Mandrake Linux to update their Apache installations immediately. What was previously thought to have been a DoS-only condition has now been proven to be more than that exploitable conditions have been discovered on both 32bit and 64bit platforms. Successful exploitation of this vulnerability may lead to the execution of arbitary code on the server running a vulnerable Apache with the permissions of the web server child process (on Mandrake Linux this is the user 'apache'). This can be used to exploit other vulnerabilities that are unrelated to Apache on the local system, and potentially permit the intruder root access. Thanks to Gobbles for proving that this exploitable condition exists. Because there are known exploits in the wild for some platforms, this update should be considered essential and should be performed immediately. All versions of Apache prior to 1.3.26 and 2.0.37 are vulnerable to this problem. MandrakeSoft has provided patched versions of Apache to correct this vulnerability. Also please note that these packages are no different than those provided in MDKSA-2002:039-1 so if you have already updated, there are no new packages to upgrade. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2002:039-2 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
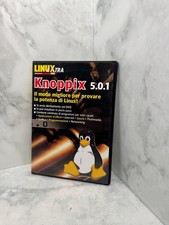
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |