|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Mandrake Local Security Checks >> MDKSA-2001:077-1: apache Vulnerability Assessment Details
|
MDKSA-2001:077-1: apache |
||
|
Check for the version of the apache package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory MDKSA-2001:077-1 (apache). A problem exists with all Apache servers prior to version 1.3.19. The vulnerablity could permit directory indexing and path discovery on the vulnerable servers with a custom crafted request consisting of a long path name created artificially by using numerous slashes. This can cause modules to misbehave and return a listing of the directory contents by avoiding the error page. Another vulnerability found by Procheckup (www.procheckup.com) was that all directories, by default, were configured as browseable so a possible hacker could list all files in the targeted directories. As well, Procheckup found that the perl-proxy/management software on port 8200 would supply dangerous information to attackers due to a perl status script that was enabled. We have disabled directory browsing by default and have disabled the perl status scripts. Update: The previous updates for 7.2 had some problems with mod_perl segfaulting and with mod_ssl under 7.1. As well, ApacheJServ was not included for 7.2 and 8.0. Other security fixes were introduced in Apache 1.3.22. A vulnerability in the split-logfile support program would permit any file with a .log extension on the system to be written to due to a specially crafted Host: header. This update provides Apache 1.3.22 for all supported platforms, and the packages for 7.1, 7.2, and Corporate Server 1.0.1 now use the same modular design as 8.0 and later versions. You will be unable to safely upgrade these packages and will need to take a few very important manual steps to ensure a proper upgrade (this is only applicable to 7.2 and earlier distributions this is not required for 8.0 and later): 1) Stop apache (service httpd stop) 2) Completely backup /etc/httpd/conf/* 3) Backup /var/log/httpd (the uninstall scripts of the previous apache versions may remove the log files) 4) Remove the currently installed apache, mod_perl, mod_ssl, and php packages from the system. You can do this using: urpme apache urpme php or (if you are using 7.2): urpme apache-common urpme php 5) Upgrade mm/mm-devel and (if you are upgrading 7.1 or Corporate Server) the new perl packages 6) Install the download upgrade packages of apache components using 'rpm -ivh *.rpm' 7) Restore your /var/log/httpd backup 8) Merge your configuration backups with the new config files (most notably you will need to edit commonhttpd.conf) 9) Start apache (service httpd start) This update also introduces PHP 4.0.6 to Linux-Mandrake 7.1, 7.2, and Corporate Server. Solution : http://wwwnew.mandriva.com/security/advisories?name=MDKSA-2001:077-1 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

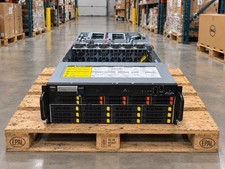
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99
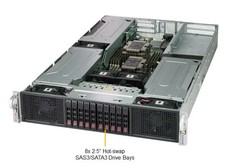
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99
|
||
|
No Discussions have been posted on this vulnerability. |