|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200703-04] Mozilla Firefox: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200703-04] Mozilla Firefox: Multiple vulnerabilities |
||
|
Mozilla Firefox: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200703-04 (Mozilla Firefox: Multiple vulnerabilities) Tom Ferris reported a heap-based buffer overflow involving wide SVG stroke widths that affects Mozilla Firefox 2 only. Various researchers reported some errors in the JavaScript engine potentially leading to memory corruption. Mozilla Firefox also contains minor vulnerabilities involving cache collision and unsafe pop-up restrictions, filtering or CSS rendering under certain conditions. Impact A possible hacker could entice a user to view a specially crafted web page that will trigger one of the vulnerabilities, possibly leading to the execution of arbitrary code. It is also possible for a possible hacker to spoof the address bar, steal information through cache collision, bypass the local files protection mechanism with pop-ups, or perform cross-site scripting attacks, leading to the exposure of sensitive information, like user credentials. Workaround There is no known workaround at this time for all of these issues, but most of them can be avoided by disabling JavaScript. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6077 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0775 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0776 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0777 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0778 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0779 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0780 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0800 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0801 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0981 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-0995 https://bugzilla.mozilla.org/show_bug.cgi?id=360493#c366 Solution: Users upgrading to the following releases of Mozilla Firefox should note that this upgrade has been found to lose the saved passwords file in some cases. The saved passwords are encrypted and stored in the 'signons.txt' file of ~/.mozilla/ and we advise our users to save that file before performing the upgrade. All Mozilla Firefox 1.5 users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-1.5.0.10" All Mozilla Firefox 1.5 binary users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-bin-1.5.0.10" All Mozilla Firefox 2.0 users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-2.0.0.2" All Mozilla Firefox 2.0 binary users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-bin-2.0.0.2" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

Apple Macintosh Plus 1MB M0001A Vintage Computer Boots Up / Floppy Disk Stuck
$99.99
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
Vintage 1998 iMac G3 M4984 Mac OS + Keyboard Working but Needs Some Repair Read
$295.00
Apple Power Macintosh PowerPC 7300/200 VTG w Keyboard Mouse Storage Drive Read
$199.99
Vintage 1992 Mac System 7.1P1 Apple Software 3.5” Floppy Disks NOS
$35.00
Apple Macintosh Plus 1MB M0001A Vintage Computer - Works
$169.99
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
185--Sonnet Crescendo G3 PPCG3-375-5-K-06 G3 Add-On Card for Vintage Mac
$99.00
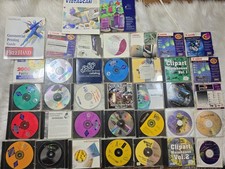
Mixed Lot Vintage Mac Windows media / Graphics / Sound Software - CDs 37 Pieces
$40.99
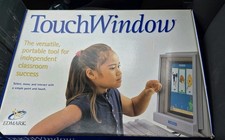
Vintage Edmark TouchWindow for Macintosh DeskTop Computer Touch Window Never Usd
$63.99
|
||
|
No Discussions have been posted on this vulnerability. |