|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200701-28] thttpd: Unauthenticated remote file access Vulnerability Assessment Details
|
[GLSA-200701-28] thttpd: Unauthenticated remote file access |
||
|
thttpd: Unauthenticated remote file access Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200701-28 (thttpd: Unauthenticated remote file access) thttpd is vulnerable to an underlying change made to the start-stop-daemon command in the current stable Gentoo baselayout package (version 1.12.6). In the new version, the start-stop-daemon command performs a "chdir /" command just before starting the thttpd process. In the Gentoo default configuration, this causes thttpd to start with the document root set to "/", the sytem root directory. Impact When thttpd starts with the document root set to the system root directory, all files on the system that are readable by the thttpd process can be remotely accessed by unauthenticated users. Workaround Alter the THTTPD_OPTS variable in /etc/conf.d/thttpd to include the "-d" option to specify the document root. Alternatively, modify the THTTPD_OPTS variable in /etc/conf.d/thttpd to specify a thttpd.conf file using the "-C" option, and then configure the "dir=" directive in that thttpd.conf file. Solution: All thttpd users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-servers/thttpd-2.25b-r5" Network Security Threat Level: Low Networks Security ID: Vulnerability Assessment Copyright: (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
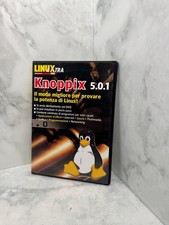
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |