|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200701-04] SeaMonkey: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200701-04] SeaMonkey: Multiple vulnerabilities |
||
|
SeaMonkey: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200701-04 (SeaMonkey: Multiple vulnerabilities) An anonymous researcher found evidence of memory corruption in the way SeaMonkey handles certain types of SVG comment DOM nodes. Georgi Guninski and David Bienvenu discovered buffer overflows in the processing of long "Content-Type:" and long non-ASCII MIME email headers. Additionally, Frederik Reiss discovered a heap-based buffer overflow in the conversion of a CSS cursor. Several other issues with memory corruption were also fixed. SeaMonkey also contains less severe vulnerabilities involving JavaScript and Java. Impact A possible hacker could entice a user to load malicious JavaScript or a malicious web page with a SeaMonkey application, possibly leading to the execution of arbitrary code with the rights of the user running those products. A possible hacker could also perform cross-site scripting attacks, leading to the exposure of sensitive information, like user credentials. Note that the execution of JavaScript or Java applets is disabled by default in the SeaMonkey email client, and enabling it is strongly discouraged. Workaround There are no known workarounds for all the issues at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6497 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6498 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6499 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6500 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6501 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6502 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6503 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6504 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6505 Solution: All SeaMonkey users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/seamonkey-1.0.7" Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

AMD Ryzen 5 5500 Processor ( read Description)
$59.00
(LOT OF 20) Intel Core i5-8400 CPU 2.80GHz Desktop Processor (SR3QT)
$700.00
INTEL CORE I9-10940X X-SERIES PROCESSOR | 3.30GHZ | SRGSH
$179.99
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
Intel Core i5-12500T SRL5W 2GHz 18MB 6 Core Socket LGA1700 Desktop CPU Processor
$114.99
Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
Intel Core i7-3770K 3.5 GHz Processor
$39.00
Intel Core i7-9700K Octa-Core 3.6 GHz Desktop CPU
$99.99
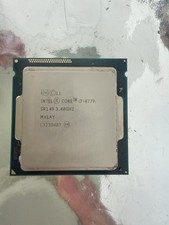
Intel Core i7-4770 3.40GHz Quad Core SR149 LGA 1150 CPU Processor tested
$35.00
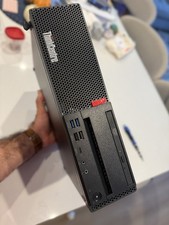
Lenovo ThinkCentre M920s SFF Barebones PC Motherboard PSU DVD No CPU RAM SSD
$27.99
|
||
|
No Discussions have been posted on this vulnerability. |