|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200701-02] Mozilla Firefox: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200701-02] Mozilla Firefox: Multiple vulnerabilities |
||
|
Mozilla Firefox: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200701-02 (Mozilla Firefox: Multiple vulnerabilities) An anonymous researcher found evidence of memory corruption in the way Mozilla Firefox handles certain types of SVG comment DOM nodes. Additionally, Frederik Reiss discovered a heap-based buffer overflow in the conversion of a CSS cursor. Other issues with memory corruption were also fixed. Mozilla Firefox also contains less severe vulnerabilities involving JavaScript and Java. Impact A possible hacker could entice a user to view a specially crafted web page that will trigger one of the vulnerabilities, possibly leading to the execution of arbitrary code. It is also possible for a possible hacker to perform cross-site scripting attacks, leading to the exposure of sensitive information, like user credentials. Workaround There are no known workarounds for all the issues at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6497 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6498 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6499 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6500 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6501 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6502 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6503 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6504 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6506 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6507 Solution: All Mozilla Firefox users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-1.5.0.9" All Mozilla Firefox binary release users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-bin-1.5.0.9" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$155.00
pfSense Firewall 16-Core Atom C3958 8GB DDR4 RAM 64GB SSD 8x 1Gbe QAT AES-NI VPN
$184.99
OPNsense pfSense 16-Core Atom C3958 16GB ECC RAM 512GB SSD 8-Port QAT AES-NI VPN
$248.00
SonicWall TZ280 Firewall 03-SSC-6933 Advanced Edition 3YR NEW SEALED
$999.99
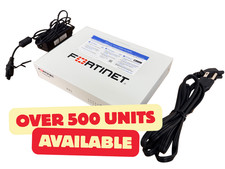
Fortinet FortiGate 60F FG-60F P24286-03-13 Network Firewall Security Appliance
$155.75
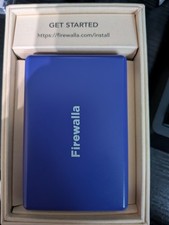
Firewalla Purple SE Cyber Security Firewall Home Business VPN…
$215.00
FortiGate-60F Network Security Firewall Fortinet - Used
$95.00
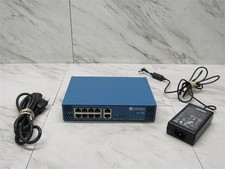
Palo Alto PA-220 Next-Gen Firewall 520-000309-00J
$40.00
NETGEAR ProSafe 8-Port Gigabit VPN Firewall FVS318G NEW IN BOX
$69.99
Cisco Meraki MX67-HW Security Appliance Firewall NEW Unused Unclaimed
$202.50
|
||
|
No Discussions have been posted on this vulnerability. |