|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200612-11] AMD64 x86 emulation base libraries: OpenSSL multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200612-11] AMD64 x86 emulation base libraries: OpenSSL multiple vulnerabilities |
||
|
AMD64 x86 emulation base libraries: OpenSSL multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200612-11 (AMD64 x86 emulation base libraries: OpenSSL multiple vulnerabilities) Tavis Ormandy and Will Drewry, both of the Google Security Team, discovered that the SSL_get_shared_ciphers() function contains a buffer overflow vulnerability, and that the SSLv2 client code contains a flaw leading to a crash. Additionally, Dr. Stephen N. Henson found that the ASN.1 handler contains two Denial of Service vulnerabilities: while parsing an invalid ASN.1 structure and while handling certain types of public key. Impact A possible hacker could trigger the buffer overflow by sending a malicious suite of ciphers to an application using the vulnerable function, and thus execute arbitrary code with the rights of the user running the application. A possible hacker could also consume CPU and/or memory by exploiting the Denial of Service vulnerabilities. Finally, a malicious server could crash a SSLv2 client through the SSLv2 vulnerability. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-2937 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-2940 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3738 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-4343 Solution: All AMD64 x86 emulation base libraries users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=app-emulation/emul-linux-x86-baselibs-2.5.5" Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00
Western Digital 0B36404 Ultrastar DC HC320 8TB 7200RPM SATA HDD, HUS728T8TALE6L4
$250.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
Seagate Exos ST20000NM003C 20TB CMR 7200RPM SATA6Gb/s 3.5" Enterprise Hard Drive
$509.99
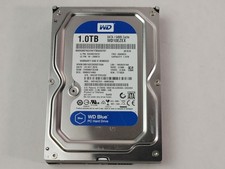
Western Digital WD Blue WD10EZEX 1 TB 3.5" SATA III Desktop Hard Drive
$23.99
Dell ST6000NM0034 1HT27Z-150 NWCCG 6TB SAS 3.5 7.2K ENTERPRISE SERVER DRIVE
$68.99
Seagate Exos ST2000NX0253 HDD 2TB SATA 7.2K 2.5" 512b/s
$55.00
DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95
(ST8000NM0045) SEAGATE ENTERPRISE 8TB 7200RPM 4Kn SATA 6Gb/s 3.5" HARD DRIVE
$199.99
|
||
|
No Discussions have been posted on this vulnerability. |