|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200611-26] ProFTPD: Remote execution of arbitrary code Vulnerability Assessment Details
|
[GLSA-200611-26] ProFTPD: Remote execution of arbitrary code |
||
|
ProFTPD: Remote execution of arbitrary code Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200611-26 (ProFTPD: Remote execution of arbitrary code) Evgeny Legerov discovered a stack-based buffer overflow in the s_replace() function in support.c, as well as a buffer overflow in in the mod_tls module. Additionally, an off-by-two error related to the CommandBufferSize configuration directive was reported. Impact An authenticated attacker could exploit the s_replace() vulnerability by uploading a crafted .message file or sending specially crafted commands to the server, possibly resulting in the execution of arbitrary code with the rights of the user running ProFTPD. An unauthenticated attacker could send specially crafted data to the server with mod_tls enabled which could result in the execution of arbitrary code with the rights of the user running ProFTPD. Finally, the off-by-two error related to the CommandBufferSize configuration directive was fixed - exploitability of this error is disputed. Note that the default configuration on Gentoo is to run ProFTPD as an unprivileged user, and has mod_tls disabled. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-5815 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6170 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-6171 Solution: All ProFTPD users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=net-ftp/proftpd-1.3.0a" Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

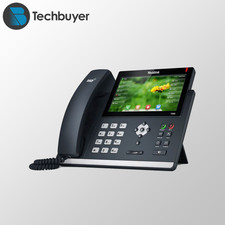
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
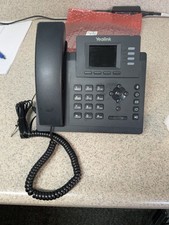
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
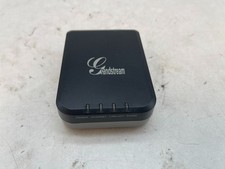
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
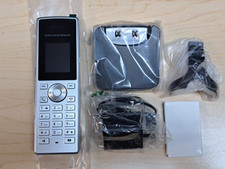
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28

Cisco / Linksys SPA2102 VoIP 2FXS Phone Adapter with Router (unlocked)
$18.99
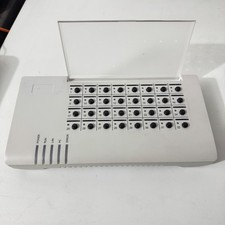
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
Poly CCX 400 Desktop Business Media Phone VoIP 2200-49700-019
$49.99
|
||
|
No Discussions have been posted on this vulnerability. |