|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200609-11] BIND: Denial of Service Vulnerability Assessment Details
|
[GLSA-200609-11] BIND: Denial of Service |
||
|
BIND: Denial of Service Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200609-11 (BIND: Denial of Service) Queries for SIG records will cause an assertion error if more than one SIG RRset is returned. Additionally, an INSIST failure can be triggered by sending multiple recursive queries if the response to the query arrives after all the clients looking for the response have left the recursion queue. Impact A possible hacker having access to a recursive server can crash the server by querying the SIG records where there are multiple SIG RRsets, or by sending many recursive queries in a short time. The exposure can be lowered by restricting the clients that can ask for recursion. An attacker can also crash an authoritative server serving a DNSSEC zone in which there are multiple SIG RRsets. Workaround There are no known workarounds at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-4095 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-4096 Solution: All BIND 9.3 users should update to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=net-dns/bind-9.3.2-r4" All BIND 9.2 users should update to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=net-dns/bind-9.2.6-r4" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

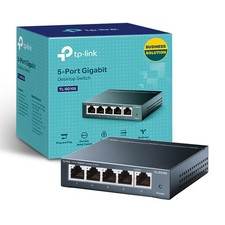
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
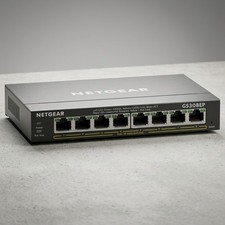
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
TP-Link TL-SG105, 5 Port Gigabit Unmanaged Ethernet Switch, Network Hub, Ethern
$15.25
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Linksys LGS328MPC 24-Port Managed Gigabit PoE+ Switch with 4 10G SFP+ Uplinks
$224.95
|
||
|
No Discussions have been posted on this vulnerability. |