|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200608-03] Mozilla Firefox: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200608-03] Mozilla Firefox: Multiple vulnerabilities |
||
|
Mozilla Firefox: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200608-03 (Mozilla Firefox: Multiple vulnerabilities) Impact A user can be enticed to open specially crafted URLs, visit webpages containing malicious JavaScript or execute a specially crafted script. These events could lead to the execution of arbitrary code, or the installation of malware on the user's computer. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3113 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3677 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3801 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3802 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3803 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3805 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3806 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3807 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3808 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3809 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3810 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3811 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2006-3812 Solution: All Mozilla Firefox users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-1.5.0.5" Users of the binary package should upgrade as well: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-bin-1.5.0.5" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

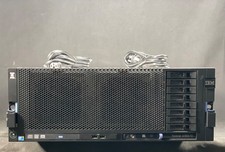
IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
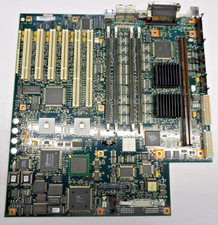
Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$179.99
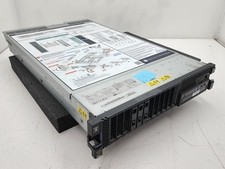
IBM Power 8 S822L Server 8247-22L POWER8 Enterprise 256GB RAM 2x 00KV626 CPU
$999.99
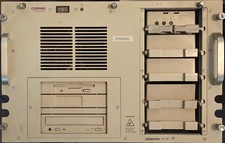
Compaq ProLiant 1500R 5/100 rack server, Series 3155, with IBM 2.1GB HD, VINTAGE
$295.00
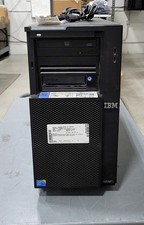
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$110.30
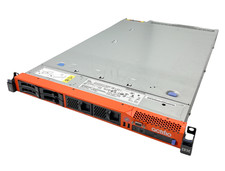
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$150.00
Rare Vintage IBM 93ZZ PowerPC Server Board - MCM Ceramic CPU - 40N1844 - 1.1 lbs
$49.99
Lot of 3 IBM 00JY196 ServeRAID M1210 PCI Express SAS SATA Storage Controller
$68.99
|
||
|
No Discussions have been posted on this vulnerability. |