|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200601-02] KPdf, KWord: Multiple overflows in included Xpdf code Vulnerability Assessment Details
|
[GLSA-200601-02] KPdf, KWord: Multiple overflows in included Xpdf code |
||
|
KPdf, KWord: Multiple overflows in included Xpdf code Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200601-02 (KPdf, KWord: Multiple overflows in included Xpdf code) KPdf and KWord both include Xpdf code to handle PDF files. This Xpdf code is vulnerable to several heap overflows (GLSA 200512-08) as well as several buffer and integer overflows discovered by Chris Evans (CESA-2005-003). Impact A possible hacker could entice a user to open a specially crafted PDF file with Kpdf or KWord, potentially resulting in the execution of arbitrary code with the rights of the user running the affected application. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CAN-2005-3191 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CAN-2005-3192 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CAN-2005-3193 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3624 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3625 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3626 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3627 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3628 http://www.gentoo.org/security/en/glsa/glsa-200512-08.xml http://www.kde.org/info/security/advisory-20051207-2.txt http://scary.beasts.org/security/CESA-2005-003.txt Solution: All kdegraphics users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=kde-base/kdegraphics-3.4.3-r3" All Kpdf users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=kde-base/kpdf-3.4.3-r3" All KOffice users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=app-office/koffice-1.4.2-r6" All KWord users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=app-office/kword-1.4.2-r6" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

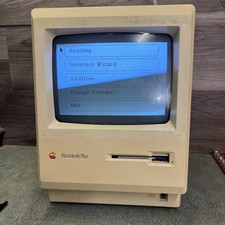
Apple Macintosh Plus 1MB M0001A Vintage Computer Boots Up / Floppy Disk Stuck
$99.99
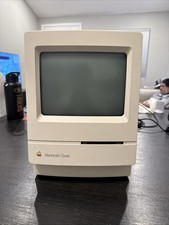
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
Vintage 1998 iMac G3 M4984 Mac OS + Keyboard Working but Needs Some Repair Read
$295.00
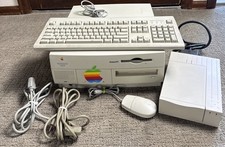
Apple Power Macintosh PowerPC 7300/200 VTG w Keyboard Mouse Storage Drive Read
$199.99
Macintosh MacTerminal M0521 Version 1.0. Vintage Apple software 1984 Sealed
$129.99
Vintage 1992 Mac System 7.1P1 Apple Software 3.5” Floppy Disks NOS
$35.00
185--Sonnet Crescendo G3 PPCG3-375-5-K-06 G3 Add-On Card for Vintage Mac
$90.00
Apple Macintosh Plus 1MB M0001A Vintage Computer - Works
$169.99
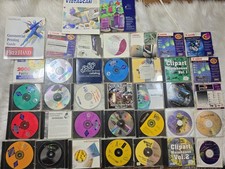
Mixed Lot Vintage Mac Windows media / Graphics / Sound Software - CDs 37 Pieces
$40.99
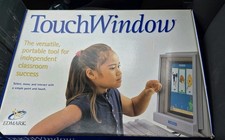
Vintage Edmark TouchWindow for Macintosh DeskTop Computer Touch Window Never Usd
$63.99
|
||
|
No Discussions have been posted on this vulnerability. |