|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200510-25] Ethereal: Multiple vulnerabilities in protocol dissectors Vulnerability Assessment Details
|
[GLSA-200510-25] Ethereal: Multiple vulnerabilities in protocol dissectors |
||
|
Ethereal: Multiple vulnerabilities in protocol dissectors Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200510-25 (Ethereal: Multiple vulnerabilities in protocol dissectors) There are numerous vulnerabilities in versions of Ethereal prior to 0.10.13, including: The SLIM3 and AgentX dissectors could overflow a buffer (CVE-2005-3243). iDEFENSE discovered a buffer overflow in the SRVLOC dissector (CVE-2005-3184). Multiple potential crashes in many dissectors have been fixed, see References for further details. Furthermore an infinite loop was discovered in the IRC protocol dissector of the 0.10.13 release (CVE-2005-3313). Impact A possible hacker might be able to use these vulnerabilities to crash Ethereal or execute arbitrary code with the permissions of the user running Ethereal, which could be the root user. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3184 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3241 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3242 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3243 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3244 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3245 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3246 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3247 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3248 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3249 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3313 http://www.ethereal.com/appnotes/enpa-sa-00021.html Solution: All Ethereal users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=net-analyzer/ethereal-0.10.13-r1" Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

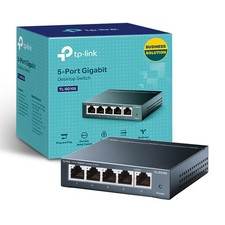
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
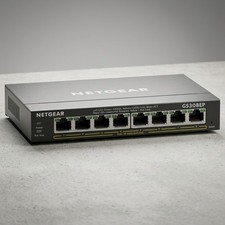
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
TP-Link TL-SG105, 5 Port Gigabit Unmanaged Ethernet Switch, Network Hub, Ethern
$15.25
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Cisco WS-C3650-12X48UR-L 48-Port Stackable Layer 3 8x10G SFP+ Port Switch
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |