|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200507-24] Mozilla Suite: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200507-24] Mozilla Suite: Multiple vulnerabilities |
||
|
Mozilla Suite: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200507-24 (Mozilla Suite: Multiple vulnerabilities) The following vulnerabilities were found and fixed in the Mozilla Suite: "moz_bug_r_a4" and "shutdown" discovered that the Mozilla Suite was improperly cloning base objects (MFSA 2005-56). "moz_bug_r_a4" reported that the suite failed to validate XHTML DOM nodes properly (MFSA 2005-55). Secunia reported that alerts and prompts scripts are presented with the generic title [JavaScript Application] which could lead to tricking a user (MFSA 2005-54). Andreas Sandblad of Secunia reported that top.focus() can be called in the context of a child frame even if the framing page comes from a different origin and has overridden the focus() routine (MFSA 2005-52). Secunia reported that a frame-injection spoofing bug which was fixed in earlier versions, was accidently bypassed in Mozilla Suite 1.7.7 (MFSA 2005-51). "shutdown" reported that InstallVersion.compareTo() might be exploitable. When it gets an object rather than a string, the browser would generally crash with an access violation (MFSA 2005-50). Matthew Mastracci reported that by forcing a page navigation immediately after calling the install method can end up running in the context of the new page selected by the attacker (MFSA 2005-48). "moz_bug_r_a4" reported that XBL scripts run even when Javascript is disabled (MFSA 2005-46). Omar Khan, Jochen, "shutdown" and Matthew Mastracci reported that the Mozilla Suite incorrectly distinguished between true events like mouse clicks or keystrokes and synthetic events generated by a web content (MFSA 2005-45). Impact A remote attacker could craft malicious web pages that would leverage these issues to inject and execute arbitrary javascript code with elevated rights, steal cookies or other information from web pages, or spoof content. Workaround There is no known workaround at this time. References: http://www.mozilla.org/projects/security/known-vulnerabilities.html#Mozilla Solution: All Mozilla Suite users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-1.7.10" All Mozilla Suite binary users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-bin-1.7.10" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |


Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00
Dell PowerEdge FC430 Blade Server 2x Xeon E5-2630v4 20 Cores FX2 FX2s No RAM/HDD
$119.99
Dell PowerEdge M630 Blade Server 2x Xeon E5-2680 v4, 2F3MP , 4GDP5 ,R10KJ ,JVFVR
$95.20
Dell PowerEdge M620 Blade Server 2x Xeon E5-2680v2 2.8ghz 20-Cores | 128GB
$149.99
NETAPP HCI NAF-1701 SuperMicro Server 4X BLADE H410C 8X GOLD 5120 4 NODE SERVER
$1499.97
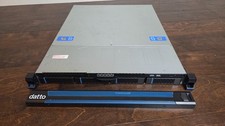
Datto S4P10 1U Blade Rack Server Intel Xeon D-2143IT 2.20GHz 48GB DDR4 4-Bay PSU
$229.95
Dell Poweredge C6400 24x 2.5’’ 2x 2400W 4x C6420 Nodes H330 | 2x SFP | 8x Trays
$799.99
Dell PowerEdge VRTX 2.5"x25 Bay Blade Enclosure 4x1600W + 4X M640 (4X Blades)
$1599.99
Dell PowerEdge M640 Blade Barebone Server Dell P/N: HHB006 Tested Working
$149.99
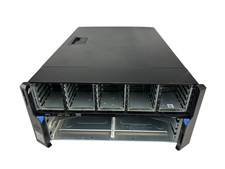
Dell Poweredge VRTX 25Bay 2.5" 2x PERC 8, 2xCMC, I/O 1GB Pass Through, 4x PS
$578.08
|
||
|
No Discussions have been posted on this vulnerability. |