|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200507-17] Mozilla Thunderbird: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200507-17] Mozilla Thunderbird: Multiple vulnerabilities |
||
|
Mozilla Thunderbird: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200507-17 (Mozilla Thunderbird: Multiple vulnerabilities) The following vulnerabilities were found and fixed in Mozilla Thunderbird: "moz_bug_r_a4" and "shutdown" discovered that Thunderbird was improperly cloning base objects (MFSA 2005-56). "moz_bug_r_a4" also reported that Thunderbird was overly trusting contents, permiting privilege escalation via property overrides (MFSA 2005-41, 2005-44), that it failed to validate XHTML DOM nodes properly (MFSA 2005-55), and that XBL scripts ran even when Javascript is disabled (MFSA 2005-46). "shutdown" discovered a possibly exploitable crash in InstallVersion.compareTo (MFSA 2005-50). Andreas Sandblad from Secunia reported that a child frame can call top.focus() even if the framing page comes from a different origin and has overridden the focus() routine (MFSA 2005-52). Georgi Guninski reported missing Install object instance checks in the native implementations of XPInstall-related JavaScript objects (MFSA 2005-40). Finally, Vladimir V. Perepelitsa discovered a memory disclosure bug in JavaScript's regular expression string replacement when using an anonymous function as the replacement argument (CVE-2005-0989 and MFSA 2005-33). Impact A remote attacker could craft malicious email messages that would leverage these issues to inject and execute arbitrary script code with elevated rights or help in stealing information. Workaround There are no known workarounds for all the issues at this time. References: http://www.mozilla.org/projects/security/known-vulnerabilities.html#Thunderbird http://www.cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0989 Solution: All Mozilla Thunderbird users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=mail-client/mozilla-thunderbird-1.0.5" All Mozilla Thunderbird binary users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=mail-client/mozilla-thunderbird-bin-1.0.5" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

External SSD 1TB 2TB 4TB Portable Hard Drive USB 3.0 Type-C High Speed PC Mac
$19.99
Dell Latitude 14" Laptop Computer Intel i5 Up To 32GB RAM 1TB SSD Windows 11 Pro
$316.61

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Dell Latitude 14" Laptop Computer Intel i7 Up To 32GB RAM 1TB SSD Windows 11 Pro
$349.48

Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99
SAMSUNG T7 Portable SSD 1TB Indigo Blue USB 3.2 Gen2 External MU-PC1T0H/AM
$159.99
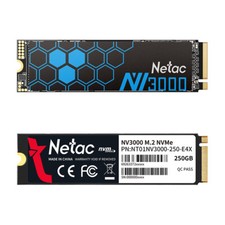
Netac 2TB 1TB 500GB Internal SSD M.2 NVMe PCIe3.0 Solid State Drive lot
$129.99
Lenovo Legion 5 Gaming 15.1" WQXGA OLED 165Hz Core i9-14900HX 16GB 1TB RTX 5070
$1469.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
Microsoft Surface Laptop Studio 14.4''(1TB SSD Intel Core i7-11370H 3.3GHz 32GB)
$540.00
|
||
|
No Discussions have been posted on this vulnerability. |