|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200507-14] Mozilla Firefox: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200507-14] Mozilla Firefox: Multiple vulnerabilities |
||
|
Mozilla Firefox: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200507-14 (Mozilla Firefox: Multiple vulnerabilities) The following vulnerabilities were found and fixed in Mozilla Firefox: "moz_bug_r_a4" and "shutdown" discovered that Firefox was improperly cloning base objects (MFSA 2005-56). Michael Krax reported that Firefox was not correctly handling JavaScript URLs from external applications (MFSA 2005-53), and that the "Set as wallpaper" function in versions 1.0.3 and 1.0.4 could be abused to load JavaScript (MFSA 2005-47). Several researchers reported ways to trick Firefox into accepting events generated by web content (MFSA 2005-45). Kohei Yoshino discovered a new way to inject script from the sidebar panel using data: (MFSA 2005-49). "moz_bug_r_a4" reported that Firefox failed to validate XHTML DOM nodes properly (MFSA 2005-55), and that XBL scripts ran even when Javascript is disabled (MFSA 2005-46). "shutdown" discovered a possibly exploitable crash in InstallVersion.compareTo (MFSA 2005-50). Finally, Secunia discovered that a child frame can call top.focus() even if the framing page comes from a different origin and has overridden the focus() routine (MFSA 2005-52), and that the frame injection spoofing bug fixed in 1.0.2 was mistakenly reintroduced in 1.0.3 and 1.0.4 (MFSA 2005-51). Impact A remote attacker could craft malicious web pages that would leverage these issues to inject and execute arbitrary script code with elevated rights, steal cookies or other information from web pages, or spoof content. Workaround There are no known workarounds for all the issues at this time. References: http://www.mozilla.org/projects/security/known-vulnerabilities.html#Firefox Solution: All Mozilla Firefox users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-1.0.5" All Mozilla Firefox binary users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-bin-1.0.5" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

GIGABYTE A520M DS3H AC AMD AM4 Motherboard mATX
$59.99
GIGABYTE Z790 AORUS ELITE AX LGA 1700 Intel Z790 ATX Motherboard with DDR5
$189.99
Intel H310 LGA1151 8-9th Gen DDR4 M.2 NVMe mATX Motherboard IO Shield Battery
$54.99
ASUS PRIME Z490-V Motherboard Intel Z490 10th gen DDR4 LGA 1200 ATX w/ IO Shield
$84.99
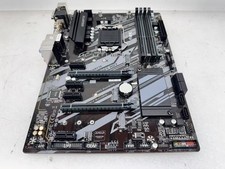
GIGABYTE B365 HD3 LGA1151 Intel 9th Gen motherboard
$59.99
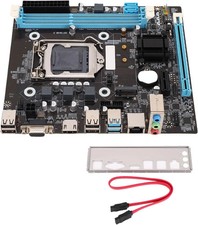
Intel H81 Motherboard M.2 NVMe LGA 1150 mATX w/ IO Shield (Random Slot Color)
$29.90
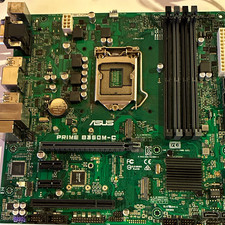
ASUS PRIME B360M-C MicroATX Intel LGA1151 DDR4 HDMI VGA USB RJ-45 Audio
$34.99
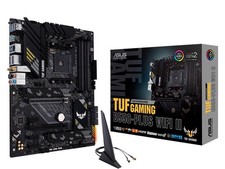
ASUS TUF GAMING B550-PLUS WIFI II AM4 AMD B550 ATX AMD Motherboard
$95.99
ASRock Z370 Pro4 LGA 1151 Z370 HDMI USB 3.1 2 Ultra M.2 DDR4 ATX Motherboard
$75.00
Dell XPS 8940 Desktop Motherboard Intel H470 LGA1200 DDR4 K3CM7 KV3RP 427JK
$154.99
|
||
|
No Discussions have been posted on this vulnerability. |