|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200503-31] Mozilla Firefox: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200503-31] Mozilla Firefox: Multiple vulnerabilities |
||
|
Mozilla Firefox: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200503-31 (Mozilla Firefox: Multiple vulnerabilities) The following vulnerabilities were found and fixed in Mozilla Firefox: Mark Dowd from ISS X-Force reported an exploitable heap overrun in the GIF processing of obsolete Netscape extension 2 (CVE-2005-0399) Kohei Yoshino discovered that a page bookmarked as a sidebar could bypass rights control (CVE-2005-0402) Michael Krax reported a new way to bypass XUL security restrictions through drag-and-drop of items like scrollbars (CVE-2005-0401) Impact The GIF heap overflow could be triggered by a malicious GIF image that would end up executing arbitrary code with the rights of the user running Firefox By tricking the user into bookmarking a malicious page as a Sidebar, a remote attacker could potentially execute arbitrary code with the rights of the user running the browser By setting up a malicious website and convincing users to obey very specific drag-and-drop instructions, attackers may leverage drag-and-drop features to bypass XUL security restrictions, which could be used as a stepping stone to exploit other vulnerabilities Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0399 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0401 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0402 http://www.mozilla.org/projects/security/known-vulnerabilities.html Solution: All Mozilla Firefox users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-1.0.2" All Mozilla Firefox binary users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-firefox-bin-1.0.2" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

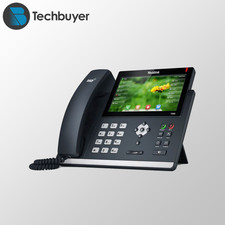
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
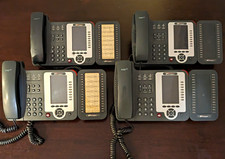
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
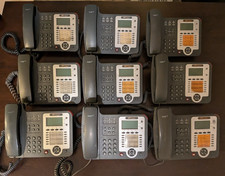
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
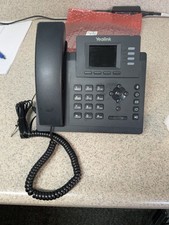
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
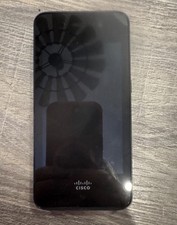
NEW Cisco CP-840 Wireless WiFi IP VoIP Phone 840 w Battery Charger Cable
$800.00
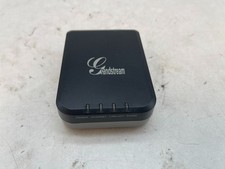
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
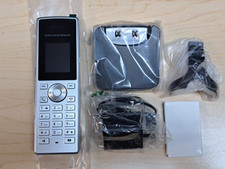
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |