|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200503-30] Mozilla Suite: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200503-30] Mozilla Suite: Multiple vulnerabilities |
||
|
Mozilla Suite: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200503-30 (Mozilla Suite: Multiple vulnerabilities) Impact The GIF heap overflow could be triggered by a malicious GIF image that would end up executing arbitrary code with the rights of the user running Mozilla. The other overflow issues, while not thought to be exploitable, would have the same impact By setting up malicious websites and convincing users to follow untrusted links or obey very specific drag-and-drop or download instructions, attackers may leverage the various spoofing issues to fake other websites to get access to confidential information, push users to download malicious files or make them interact with their browser preferences The temporary directory issue permits local attackers to overwrite arbitrary files with the rights of another local user Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-1156 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0230 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0231 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0232 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0233 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0255 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0399 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0401 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0527 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0578 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0584 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0585 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0588 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0590 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0591 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0592 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0593 http://www.mozilla.org/projects/security/known-vulnerabilities.html Solution: All Mozilla Suite users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-1.7.6" All Mozilla Suite binary users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-client/mozilla-bin-1.7.6" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99
Crucial 32GB(4 x 8GB) CT8G4DFS824A.C8FDD1 DDR4-2400 UDIMM Desktop RAM - CR352A
$89.95

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
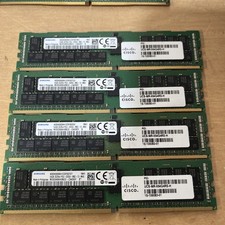
Samsung 64GB PC4-2666V-R 2S2Rx4 DDR4 ECC REG RDIMM - M393A8K40B22-CWD6Y
$270.00
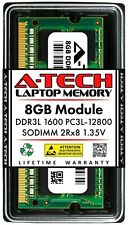
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
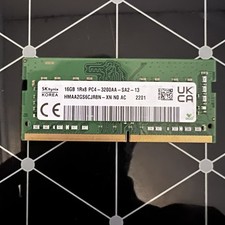
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
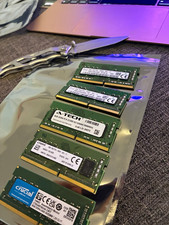
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
TeamGroup T-FORCE VULCAN Z 16GB (2 x 8GB) DDR4 3000Mz (PC4 24000) Desktop Memory
$97.76
|
||
|
No Discussions have been posted on this vulnerability. |