|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200503-02] phpBB: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200503-02] phpBB: Multiple vulnerabilities |
||
|
phpBB: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200503-02 (phpBB: Multiple vulnerabilities) It was discovered that phpBB contains a flaw in the session handling code and a path disclosure bug. AnthraX101 discovered that phpBB permits local users to read arbitrary files, if the "Enable remote avatars" and "Enable avatar uploading" options are set (CVE-2005-0259). He also found out that incorrect input validation in "usercp_avatar.php" and "usercp_register.php" makes phpBB vulnerable to directory traversal attacks, if the "Gallery avatars" setting is enabled (CVE-2005-0258). Impact Remote attackers can exploit the session handling flaw to gain phpBB administrator rights. By providing a local and a remote location for an avatar and setting the "Upload Avatar from a URL:" field to point to the target file, a malicious local user can read arbitrary local files. By inserting "/../" sequences into the "avatarselect" parameter, a remote attacker can exploit the directory traversal vulnerability to delete arbitrary files. A flaw in the "viewtopic.php" script can be exploited to expose the full path of PHP scripts. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0258 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0259 http://www.phpbb.com/phpBB/viewtopic.php?f=14&t=267563 Solution: All phpBB users should upgrade to the latest available version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-apps/phpBB-2.0.13" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Computer Photo History Altair 8800 Philco 212 CDC 6600 DEC PDP-8 Apple 1 UNIVAC
$69.99
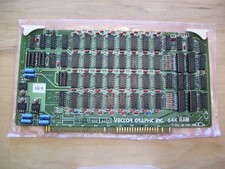
S-100 Vector Graphic 64K Ram Board (Altair, IMSAI)
$99.95
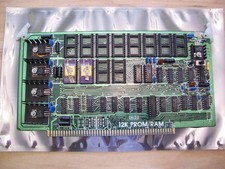
S-100 Vector Graphic 12K PROM/RAM Board (Altair, IMSAI)
$99.95
Microcomputer Builder's Bible IMSAI 8080 Z80 ADM-3A DEC LSI-11 Altair 8800 Bus
$65.00
Vintage Digital Research ZSID 1.4 8" Floppy Disk CP/M Z80 Software S-100 Altair
$69.99
640pg Best of BYTE Magazine 1984 Mac Steve Jobs Altair 8800 IBM 5100 Bob Moog
$85.00
S-100 Bus Handbook Altair 8800 IMSAI 8080 Board Schematics Xitan Pertec Cromemco
$89.99
S-100 Industrial Micro Systems 8K Static Ram (IMS, Altair, IMSAI)
$69.95
CP/M 86 1.1R 8086 Highmonitor 8 Inch Floppy Diskette 80s IMSAI Altair
$29.99
ALTAIR Bitcoin Mining Solutions PDU IEC SERIES 100-250V 30A/24A Power Distribute
$99.00
|
||
|
No Discussions have been posted on this vulnerability. |